concept Envoy Proxy in category istio

This is an excerpt from Manning's book Istio in Action.
$  kubectl apply -f chapters/chapter2/catalog-virtualservice-dark-v2.yaml
virtualservice.networking.istio.io/catalog configured
When we introduced the idea of a service mesh in Chapter 1, we established the concept of a service proxy and how this proxy is built to understand application-level constructs (e.g., application protocols like HTTP and gRPC) and supplement an application’s business logic with non-differentiating application-networking logic. This service proxy runs collocated and out of process with the application and the application talks through the service proxy whenever it wants to communicate with other services. With Istio, Envoy Proxy is the default out-of-the-box service proxy and gets deployed collocated with all application instances participating in the service mesh thus forming the service-mesh data plane. Since Envoy is such a critical component in the data plane, and in the overall service-mesh architecture, we’ll spend this chapter getting familiar with Envoy in hopes you better understand Istio and how to dig into specific components when putting together a bigger architecture or when you need to debug or troubleshoot your deployments.
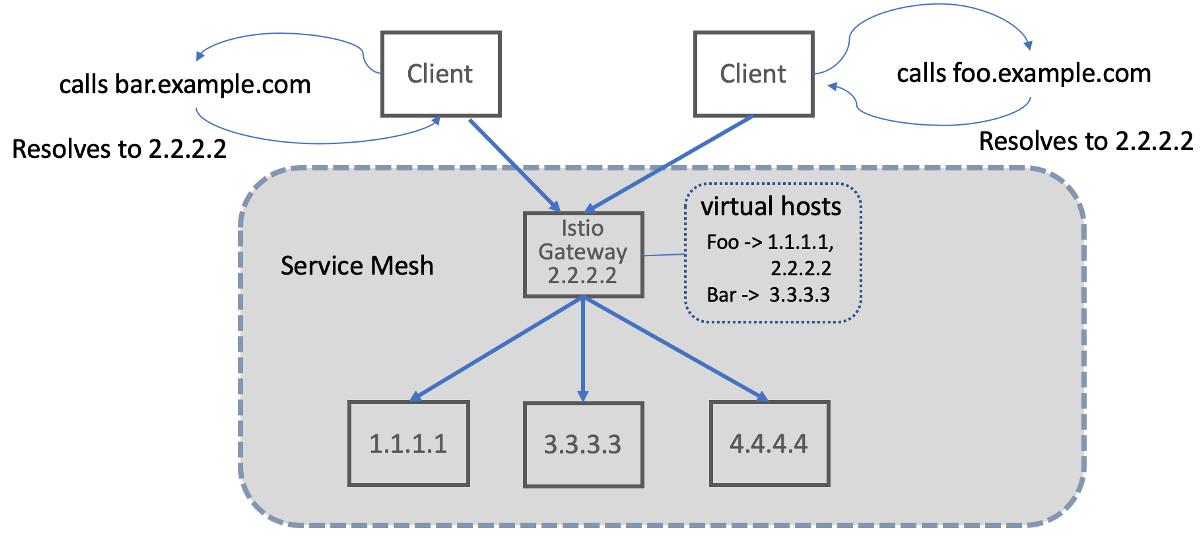
Figure 4.5. Istio Gateway plays the role of network ingress and uses Envoy Proxy to do the routing and load balancing