concept encryption in category node

This is an excerpt from Manning's book Get Programming with Node.js.
In this lesson, you learned about sessions and cookies, and saw why they’re integral parts of how data is transferred between the server and client. You also set up connect-flash to use cookies and temporarily show success and failure messages on certain views. In lesson 23, you see how to encrypt more than cookie data by implementing encryption on user passwords.
Add passport authentication and encryption for the User model
This is an excerpt from Manning's book Getting MEAN with Mongo, Express, Angular, and Node.js 2ED.
Encrypting isn’t enough, though. If several people used the word password as their password (it happens!) the encryption for each is the same. Any hackers looking through the database could see this pattern and identify potentially weak passwords.
This is where the concept of a salt comes in. A salt is a random string generated by the application for each user that’s combined with the password before encryption. The resulting encrypted value is called a hash, as illustrated in figure 11.8.
Encryption is such a common requirement that Node has a built-in module called crypto. This module comes with several methods for managing the encryption of data. In this section, we’ll look at the following two:

This is an excerpt from Manning's book Node.js in Practice.
Node has a suite of networking modules that allows you to build web and other server applications. Over the next few sections we’ll cover DNS, TCP, HTTP, and encryption.
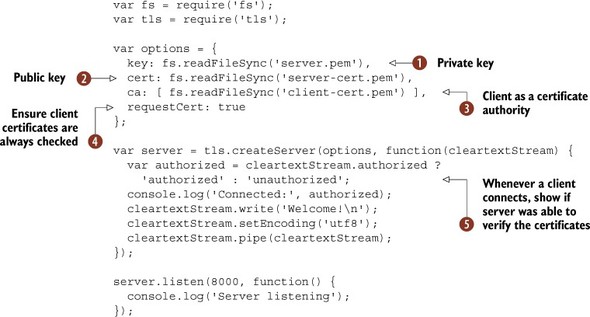
The main thing to master when working with encryption, whether it’s web servers, mail servers, or any TCP-based protocol, is how to properly set up the key and certificate files. Public key cryptography is dependent on public-private key pairs—a pair is required for both clients and servers. But an additional file is needed: the public key of the Certificate Authority (CA).