concept authentication process in category spring
appears as: authentication process, The authentication process, n authentication process

This is an excerpt from Manning's book Spring Security in Action.
Session fixation vulnerability is a more specific, high severity weakness of a web application. If present, it permits an attacker to impersonate a valid user by reusing a previously generated session ID. This vulnerability could happen if, during the authentication process, the web application does not assign a unique session ID, and this could make possible the reuse of existing session IDs. Exploiting this vulnerability consists of obtaining a valid session ID and making the intended victim’s browser use it.
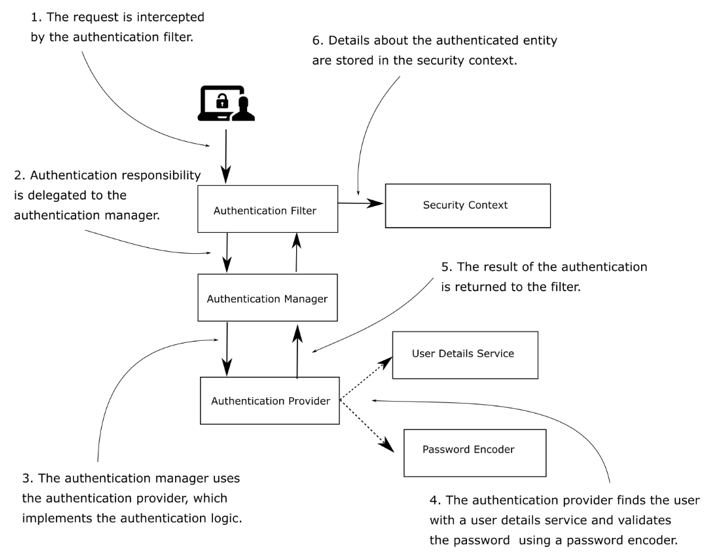
Figure 2.2 The main components acting in the authentication process for Spring Security and the relationships among them. This architecture represents the backbone of implementing authentication with Spring Security. For this reason, we’ll refer to it a lot throughout the book when discussing different implementations for authentication and authorization.
isAuthenticated() - Returns true if the authentication process ended or false if the authentication process is still in progress.