access-class applies an access control list (ACL) to Cisco IOS terminal lines, especially VTY lines. It restricts which hosts can establish management connections without filtering other traffic. section 5.2.2
Remember the operational distinction:
- Use access-list or ip access-list to create an ACL. section 5.2.2
- Use ip access-group to apply an ACL to an interface. section 5.2.2
- Use access-class to apply an ACL to VTY lines. section 5.2.2
- Place the command under line vty configuration, commonly as access-class 1 in. section 5.2.2
Restricting VTY access
Under line vty 0 4 and line vty 5 15, access-class 1 in permits only sources allowed by ACL 1. The same restriction appears in both VTY groups when all 16 lines are configured. section 5.2.2
Figure 5.5 Enabling Telnet on SW1. Users must log in with a local user account and will be logged out after 20 minutes of inactivity. Only Telnet can be used to connect to the VTY lines, and only hosts in 192.168.1.0/24 are permitted.
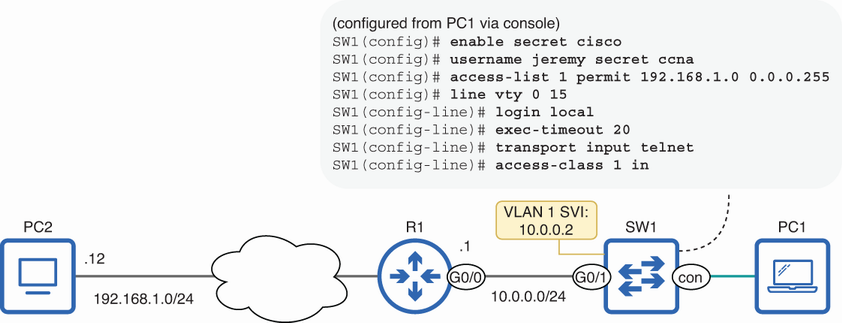
The topology summary shows the intended result: only hosts in 192.168.1.0/24 can reach the VTY lines, while Telnet remains the permitted transport. section 5.2.2
