Access-Control-Allow-Methods is a CORS response header that limits cross-origin access to selected HTTP methods, such as allowing an external origin to use only GET. section 10.1
Use the header to:
- Declare which methods a browser may accept for a cross-origin request. section 10.1
- Validate preflight behavior by checking the header returned for an HTTP OPTIONS request. section 18.7
Testing an allowed POST method
A MockMvc test sends OPTIONS to /test with Access-Control-Request-Method: POST and verifies that Access-Control-Allow-Methods equals POST. section 18.7
Figure 10.4 For simple requests, the browser sends the original request directly to the server. The browser rejects the response if the server doesn’t allow the origin. In some cases, the browser sends a preflight request to test whether the server accepts the origin. If the preflight request succeeds, the browser sends the original request.
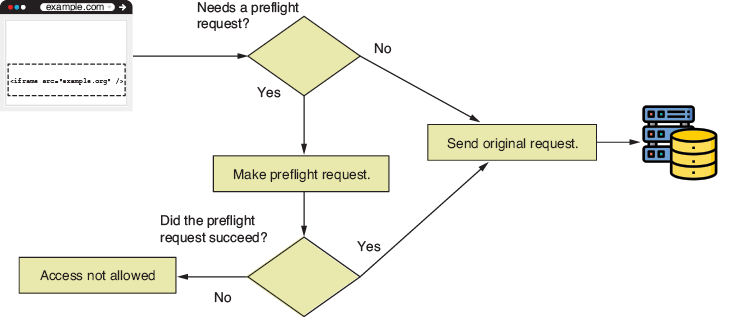
For some cross-origin requests, the browser sends a preflight request first and sends the original request only when the server permits it. section 10.1
