The OWASP API Security Top 10 is an industry-consensus awareness document that ranks critical security threats affecting web APIs. The 2023 version supports security review and design-time detection rather than replacing detailed vulnerability-mitigation guidance. section 10.2.1
The 2023 list includes these risks that can be detected partly by linting API definition files:
- API1:2023 — Broken Object Level Authorization section 10.2.1
- API2:2023 — Broken Authentication section 10.2.1
- API3:2023 — Broken Object Property Level Authorization section 10.2.1
- API4:2023 — Unrestricted Resource Consumption section 10.2.1
- API8:2023 — Security Misconfiguration section 10.2.1
Use the risks to shape API linting rules and CI/CD security checks at design time. Add runtime validation of traffic against OpenAPI definitions in an API gateway, and extend controls through DevSecOps practices and the API development life cycle. section 10.4
Figure 10.5 The Top 10 API security risks identified by OWASP
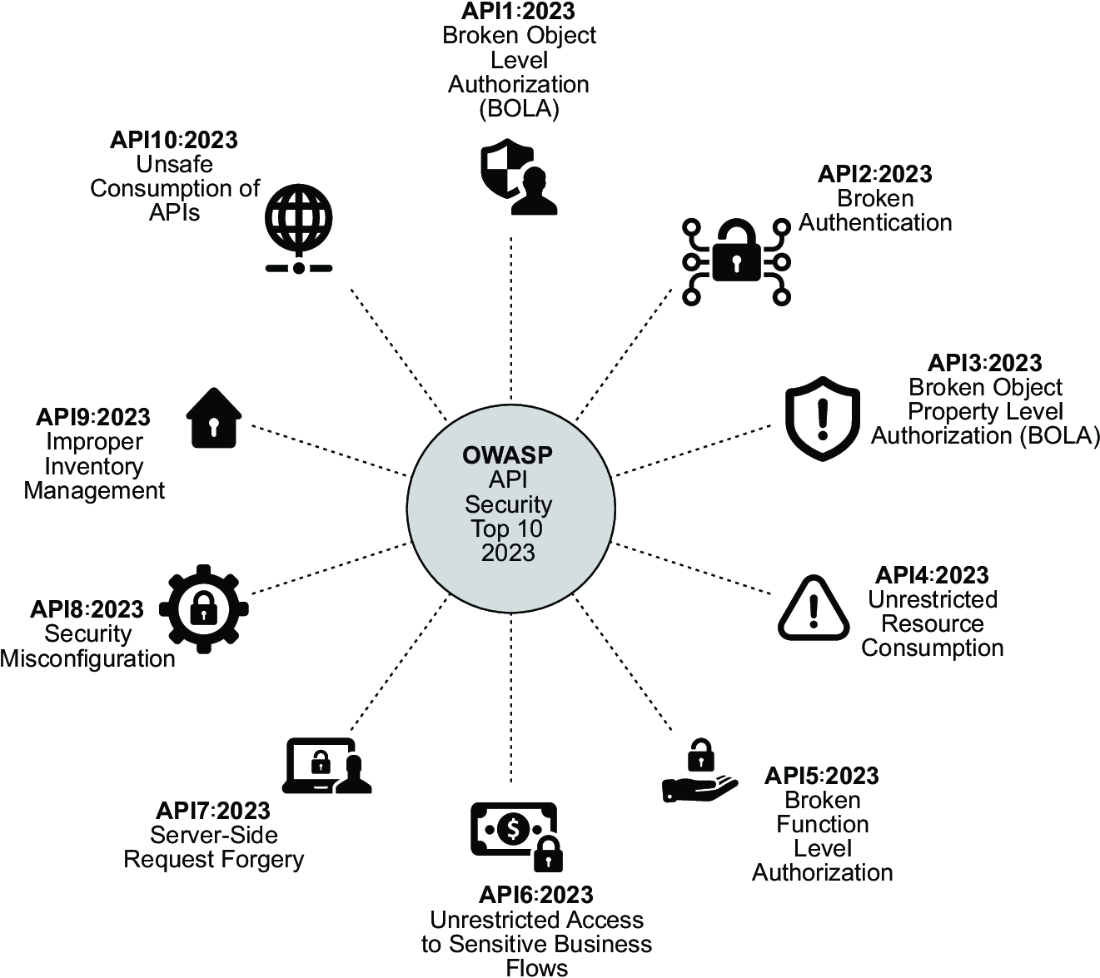
Browse the visual overview of the Top 10 API security risks identified by OWASP. section 10.2.1

