A finance reporting service needs to specify who may view its reports without duplicating organization-wide device checks. An application-specific policy defines the resources, actions, and authorities for one service or application domain. Product or engineering teams responsible for the service manage these narrow, domain-specific rules. section 15.3.3
permit(
    principal in Group::"Finance",
    action == ACME::Action::"Report:view",
    resource in Report::"internal_financials"
);
This Cedar policy permits members of the Finance group to view internal financial reports. It expresses the service’s business rule, not device posture or authentication requirements. section 15.3.3
Application policies work alongside two broader layers: foundational security policies set enterprise-wide requirements, while shared operational policies govern rules spanning multiple systems or workflows. Separating ownership lets service teams focus on domain rules while other teams maintain common controls. section 15.3.3 section 15.3
Figure 15.4 Access control in a zero-trust security architecture. The PEP collects authentication context, device posture, and other request information to create a normalized request for the policy engine. The policy engine forms an effective policy set by selecting relevant foundational, shared operational, and application policies, and then evaluates the normalized request once to make a unified authorization decision. The PEP then enforces that decision at the target resource.
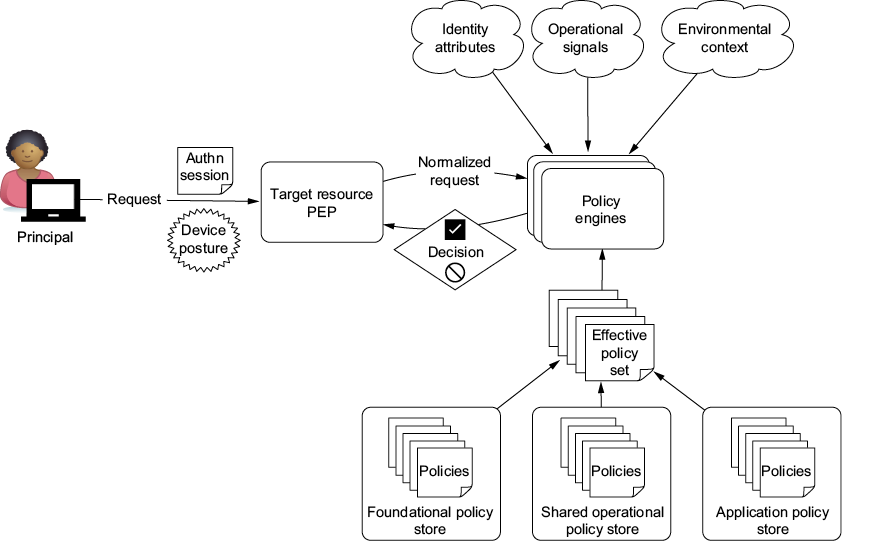
The policy enforcement point collects request context and sends a normalized request to the policy engine. The engine combines applicable policies from all three layers into one decision, which the enforcement point applies at the resource. section 15.4
An application permit does not bypass a security restriction
A finance application policy may permit a report view, but a foundational device policy can forbid the request if the laptop fails the device-posture requirement. With Cedar’s forbid-overrides-permit semantics, the overall decision is deny. section 15.4
