An authentication error occurs when submitted credentials cannot verify an identity. Spring Security returns HTTP 401 Unauthorized and does not forward the request to the endpoint. section 8.1
Distinguish authentication failure from endpoint authorization:
- A request without credentials can reach an endpoint configured with permitAll(). section 8.1
- A request containing invalid credentials still enters authentication, fails verification, and receives 401 Unauthorized. section 8.1
- Authentication runs before authorization, so permitAll() does not allow a request with failed credentials to continue. section 8.1
Invalid credentials on a public endpoint
With /hola configured using anyRequest().permitAll(), curl http://localhost:8080/hola returns Hola! with 200 OK. Supplying curl -u bill:abcde http://localhost:8080/hola instead returns a 401 Unauthorized response. section 8.1
The authorization filter allows any request to the /hola path. However, because the application first executes the authentication logic, the request is never forwarded to the authorization filter. Instead, the authentication filter replies with an HTTP 401 Unauthorized.
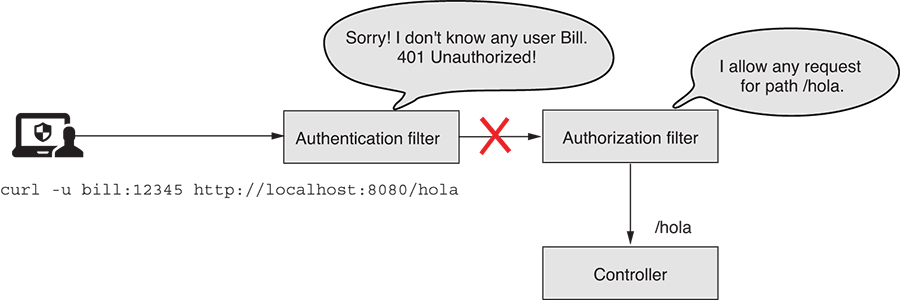
Trace how the authentication filter rejects invalid credentials before the authorization filter can apply the endpoint's permitAll() rule. section 8.1
