An authentication filter intercepts an authentication request and delegates it to the authentication manager. The manager uses an authentication provider, which applies the authentication logic and returns a response that the filter uses to configure the security context. section 2.2
The authentication flow connects these responsibilities:
- The authentication manager coordinates authentication processing. section 2.2
- The authentication provider implements the authentication logic, using UserDetailsService for user management and PasswordEncoder for password management. section 2.2
- The security context retains authentication data until the action ends, usually until a thread-per-request application sends its response. section 2.2
Authenticated endpoint request
A request such as `curl -k -u user:93a01cf0-794b-4b98-86ef-54860f36f7f3 https://localhost:8080/hello` supplies credentials for a protected endpoint and receives `Hello!` after successful authentication. section 2.2
Figure 2.2 The core elements involved in Spring Security’s authentication process and their interconnections are the focus here. This framework forms the essential structure for executing authentication using Spring Security. Throughout the book, we will frequently reference this architecture while examining various authentication and authorization strategies.
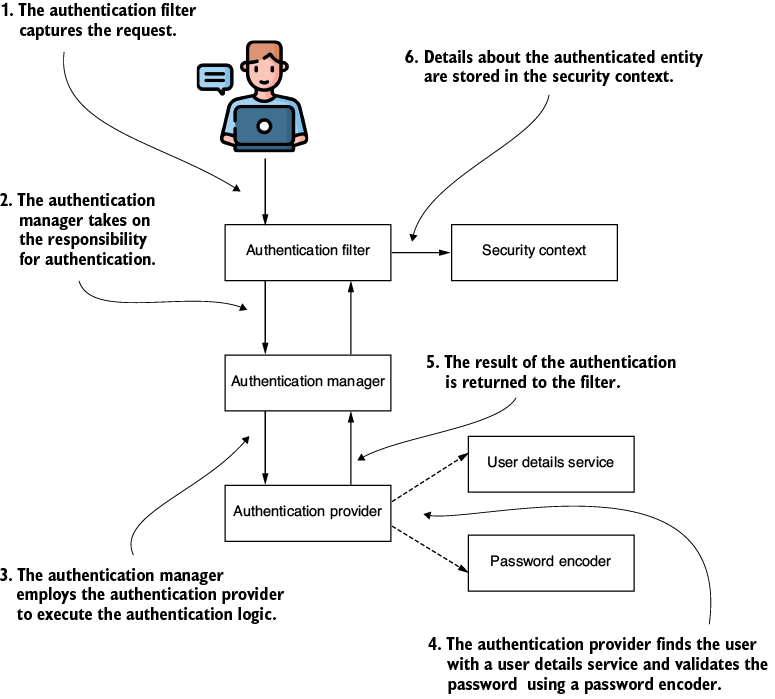
Use the architecture diagram to trace the authentication filter’s relationships with the authentication manager, provider, user details service, password encoder, and security context. section 2.2
