AuthenticationProvider is the Spring Security component that implements authentication logic. AuthenticationManager delegates requests to it, while it may use UserDetailsService for user lookup and PasswordEncoder for password validation. section 2.2 section 6.1.2
Implementations coordinate authentication through two contract methods:
- Implement authenticate(Authentication) to return a fully authenticated Authentication object when verification succeeds. section 6.1.2
- Throw an AuthenticationException when credentials or user validation fails. section 6.1.2
- Return null when the provider does not support the received authentication object, allowing other providers to evaluate it. section 6.1.2
- Implement supports(Class<?>) to identify the Authentication types the provider can process. section 6.1.2
- Remove sensitive data such as passwords from successful authentication results when it is no longer required. section 6.1.2
Custom username-and-password provider
Declare a Spring component implementing AuthenticationProvider, support UsernamePasswordAuthenticationToken, load the user through UserDetailsService, and compare credentials with PasswordEncoder. Return a token containing the user’s authorities on success; otherwise throw BadCredentialsException. Register the provider with http.authenticationProvider(authenticationProvider) and require authentication for requests. section 6.1.3 section 2.3.4
Figure 6.4 The AuthenticationManager delegates to one of the available authentication providers. The AuthenticationProvider might not support the provided authentication type. However, if it does support the object type, it might not know how to authenticate that specific object. The authentication is evaluated, and an AuthenticationProvider that can say whether or not the request is correct responds to the AuthenticationManager.
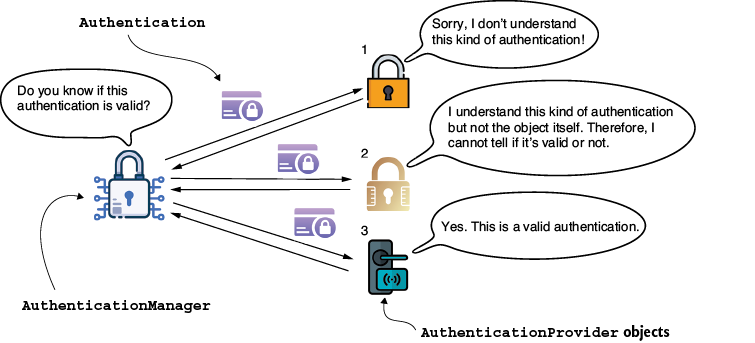
Trace how AuthenticationManager delegates to providers, how providers select supported authentication types, and how rejection produces an authentication exception. section 6.1.2
