An authorization code is a short-lived credential returned after successful user authorization. A client receives it through a redirect URI, then exchanges it for tokens. section 8.1.2
Returning a mobile login to the app
A .NET MAUI app uses the custom redirect URI auth.com.mildredsurf.stocktake://callback. After login, the identity provider returns the authorization code through that URI. WebAuthenticator receives the response, AuthBrowser extracts the code, and OidcClient processes it to return tokens to AuthService. section 8.1.2
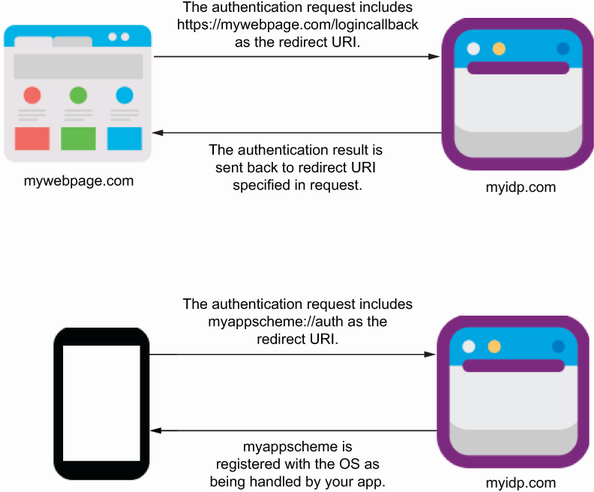
Figure 8.4 When authenticating with an IDP, a redirect URL is supplied. Upon successful authentication, a response is sent back to the redirect URL. For a web application, this redirect is usually the address of the web application where the authentication request originated. For a mobile or desktop app, the URL uses a custom scheme that the OS associated with the app, so the response from the IDP is sent to the app.
Follow the redirect from the identity provider back to a registered mobile or desktop application. section 8.1.2

