Azure Blueprints orchestrates repeatable Azure environment setups so resources follow security best practices and organizational business rules. It combines deployment and governance rather than relying on a single control. section 10.5
A blueprint can coordinate these artifacts:
- Azure Policy assignments and policy initiatives for enforceable configuration rules. section 10.5
- Resource groups and Azure resources deployed through ARM templates. section 10.5
- Least-privileged role assignments that give users access to the resources they need. section 10.5
Developer environment
Prepare a developer environment by creating its resource groups, deploying required resources, assigning security policies, and granting only the necessary roles. The resulting setup is consistent and aligned with business rules. section 10.5 section 10.9
Figure 10.5 A custom policy initiative displayed in the Regulatory Compliance dashboard in Microsoft Defender for Cloud
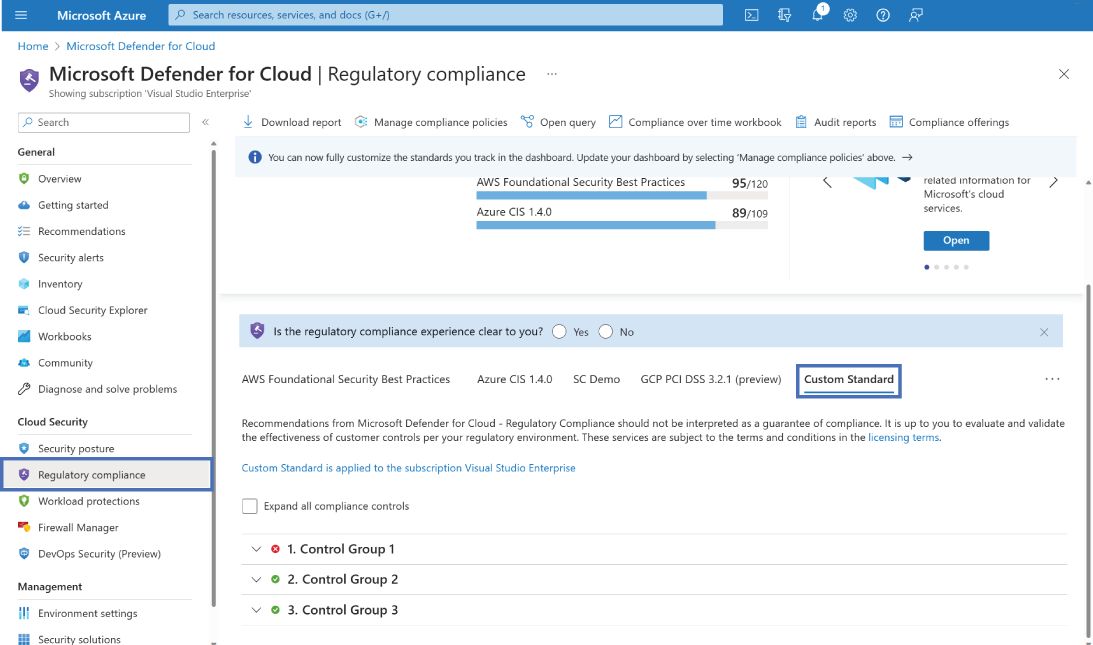
Use the compliance dashboard view to connect custom policy initiatives with centralized security-policy management. section 10.4
