Key Vault Administrator is an Azure built-in role that can perform every data plane operation on a key vault and its objects, including keys, secrets, and certificates. It is used when configuring Azure Storage with a customer-managed encryption key: the administrator grants a managed identity permission to access that key. section 5.2.2 section 5.1.6
For customer-managed key encryption, the operational relationship is:
- Assign the Key Vault Administrator role within a key vault that uses the Azure RBAC permission model. section 5.2.2
- Grant the Storage account’s user-assigned or system-assigned managed identity at least get, wrapkey, and unwrapkey permissions on the key. section 5.1.6
- Let Azure Storage authenticate through Microsoft Entra ID, wrap its account encryption key, and request unwrapping for encryption and decryption. section 5.1.6
Scope comparison
Key Vault Administrator covers all data plane operations. More focused alternatives include Key Vault Reader for metadata, Key Vault Crypto User for cryptographic operations, and Key Vault Secrets User for reading secret contents. section 5.2.2
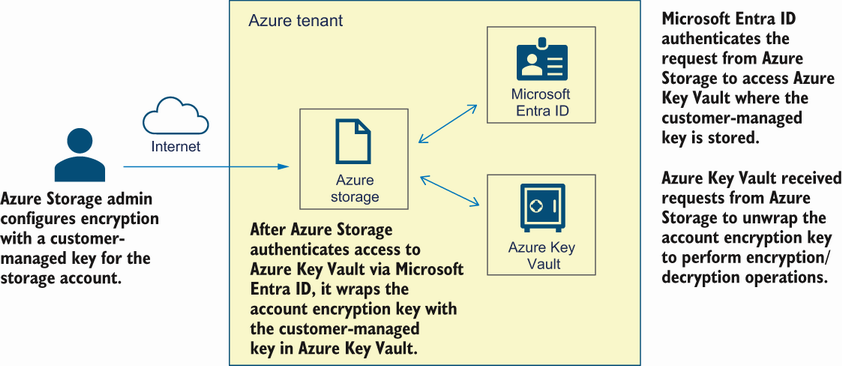
Trace how Azure Storage uses a customer-managed key in Key Vault to protect its account encryption key. section 5.1.6
