Basic authentication lets a web client authenticate with a username and password sent in the HTTP Authorization header. The header contains the Basic prefix followed by a Base64-encoded username-and-password string separated by a colon. section 2.2
Base64 only encodes the credentials; it does not encrypt or hash them. Use HTTPS to provide confidentiality while the request is in transit. section 2.2
A small Spring application can use Basic authentication with little configuration:
- Adding the Spring Security dependency causes Spring Boot to secure endpoints, create default authentication settings, and generate a password at startup. section 2.1
- The default configuration requires an authenticated user for every endpoint and uses a default UserDetailsService, PasswordEncoder, and authentication provider. section 2.2
- Define a SecurityFilterChain when endpoint authorization or authentication behavior must change; use httpBasic() to select Basic authentication explicitly. section 2.3.2 section 6.3.1
- Apply authenticated() to require credentials or permitAll() to make matching endpoints accessible without them. section 2.3.2
Calling a protected REST endpoint
For a /hello endpoint, a request without credentials returns 401 Unauthorized. Supplying credentials with curl, either through -u user:password or an Authorization header containing Basic and the Base64 value, returns the endpoint response. section 2.1
Basic authentication can be customized through HttpBasicConfigurer, including the protection-space realm name and the response for failed authentication. An AuthenticationEntryPoint can add response headers or produce a custom 401 response. section 6.3.1
Figure 2.1 Our initial application employs HTTP Basic for user authentication and authorization when accessing an endpoint. It offers a REST endpoint at a specified route (/hello). Upon a successful request, it issues an HTTP 200 status message along with a response body. This instance illustrates the default authentication and authorization mechanisms set up by Spring Security.
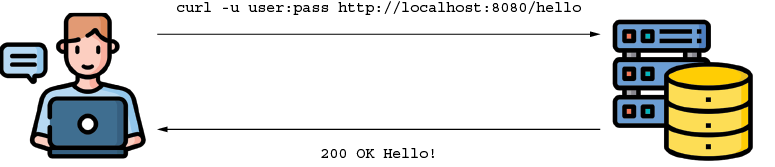
Trace the protected REST endpoint from authentication and authorization through a successful HTTP 200 response. section 2.1


