liveBook · Manning

Bastion host

As explained in Google Anthos in Action

A bastion host is a hardened intermediary host through which administrators connect to otherwise restricted systems or management networks.

A bastion host is the administrator’s entry point to the GKE on AWS management service. Administrators log in to it before performing cluster management operations, keeping access to restricted management components behind an intermediary host. section 5.2.2

Operationally, the bastion host:

  • Is deployed during initial installation of the management service. section 5.2.2
  • Receives administrator connections for GKE on AWS operations management. section 5.2.2
  • Can be avoided by using the supplied Terraform installation sample, which simplifies deployment and removes the bastion host and management server steps. section 5.2.2
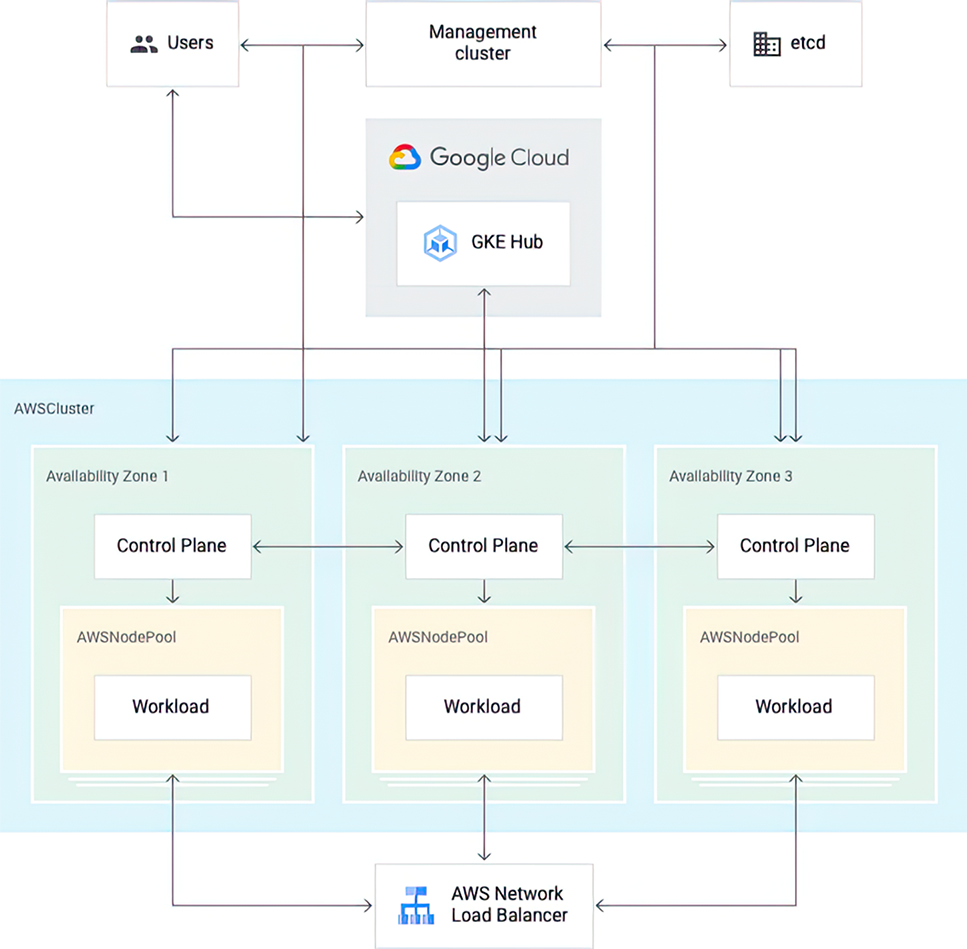
Figure 5.12 GKE on AWS architecture
05-12

Use the GKE on AWS architecture diagram to locate the bastion host within the management-service deployment. section 5.2.2


How Google Anthos in Action covers it

How deep it goes
Defines the host’s deployment and access role but does not detail hardening controls or high-availability design.
Examples
Uses the initial management-service installation and a Terraform sample that removes the bastion-host deployment step.
What it assumes
Assumes familiarity with GKE on AWS installation and its management service.
What you can do after
Operate GKE on AWS management functions by logging in to the deployed bastion host.
How it connects
Connects bastion hosts with GKE on AWS, the management service, Terraform, and AWS EC2 instances.

Also explained in

Compare how 2 books explain bastion host →

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Google Anthos in Action. The section links point to the parts of the book it draws on.