Certificate-based authentication verifies a Kubernetes user by having the API server validate a signed X.509 client certificate stored in a kubeconfig file. Kubernetes’s built-in certificate authority signs the certificate, which the client presents with API requests to prove identity. section 3.1
Use the authentication method that matches the requester:
- Human requests made with kubectl commonly use client certificates or external identity providers and map to usernames. section 3.1
- Pod-to-API requests commonly use Service Account tokens rather than user client certificates. section 3.1
- Authentication precedes authorization: after identity is established, RBAC determines whether the request is allowed. section 3.1
Figure 3.1 Using a certificate and token to access the Kubernetes API
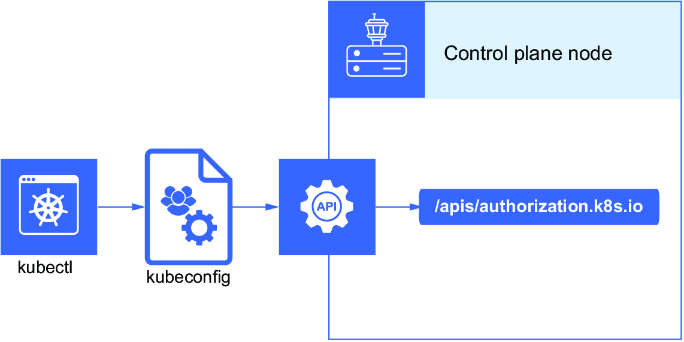
Trace how a certificate and token reach the Kubernetes API during authentication. section 3.1
