Certificate management secures service-mesh communication by issuing trusted identities for workloads. In Istio, istiod acts as the certificate authority, provisioning certificates that enable secure mutual TLS between services. section 4.3.3 section 4.3.1
Istio certificate management separates trust and signing responsibilities:
- A root certificate may sign every certificate directly, or delegate signing to a subordinate certificate authority. section 4.3.3
- The CA can use a generated self-signed root, an administrator-specified root and key, or an administrator-specified delegated-CA signing certificate and key. section 4.3.3
- Istiod combines certificate management with service discovery, configuration, routing, and authentication components supporting the Envoy sidecars. section 4.3.1
Enterprise trust integration
An enterprise can configure Istio’s CA with an existing organizational root certificate or a delegated CA signing certificate and key, keeping root-signing responsibility outside the mesh. section 4.3.3
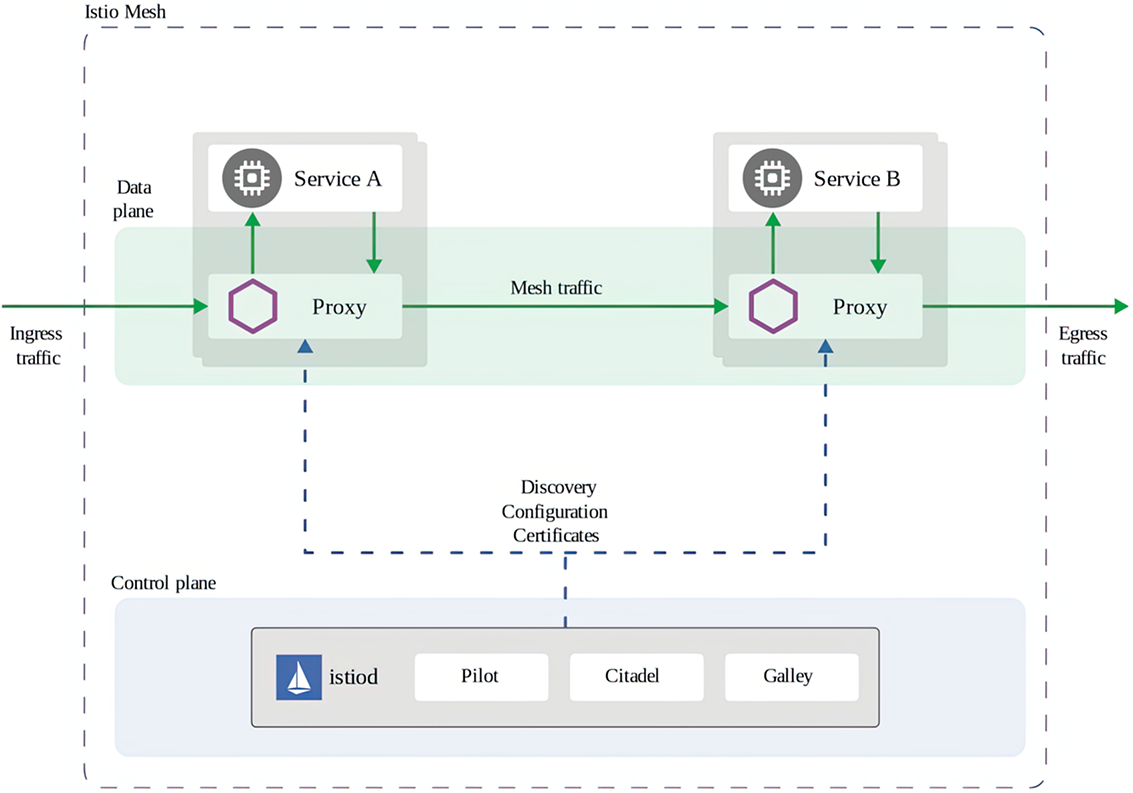
Use the detailed Istio architecture to locate istiod, sidecar proxies, and the certificate-management path within the service mesh. section 4.3.1
