A cgroup is a Linux kernel mechanism for organizing processes and controlling their resource consumption. In kind, layered cgroup and namespace setups isolate pod containers inside node containers while sharing the host kernel. section 2.1.4
Figure 2.12 kind cluster architecture, with nodes running as
containers on our local system
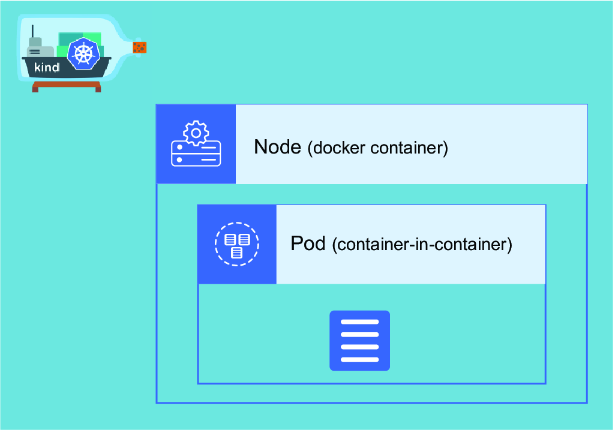
Use the architecture diagram to trace the containment layers: local system, node container, pod, and pod containers. section 2.1.4
Verify the cgroup-backed node environment with these administrator checks:
- Run `kubectl get no -o wide` to identify the node’s operating system, kernel version, and container runtime. section 2.1.4
- Enter a kind worker and inspect kubelet startup, including the cgroup v2 setup script. section 2.1.4


