A team-based authorization model makes the development team the central authorization role: individuals authenticate, but permissions primarily follow team membership. Domain-bounded teams provide the organizational boundary for platform access, resources, and governance. section 4.3.3
Apply the model by:
- Granting a developer access to the team’s platform and developer resources automatically when they join. section 4.3.3
- Maintaining access control and governance around team resources rather than accumulating ad hoc individual permissions. section 4.3.3
- Using a dedicated identity provider as an intermediary between authentication, authorization, and external systems of record. section 4.3.3
Figure 4.8 We want the IDP to be the go-between rather than the source of truth, and we will need to be able to customize the results from the authorization service.
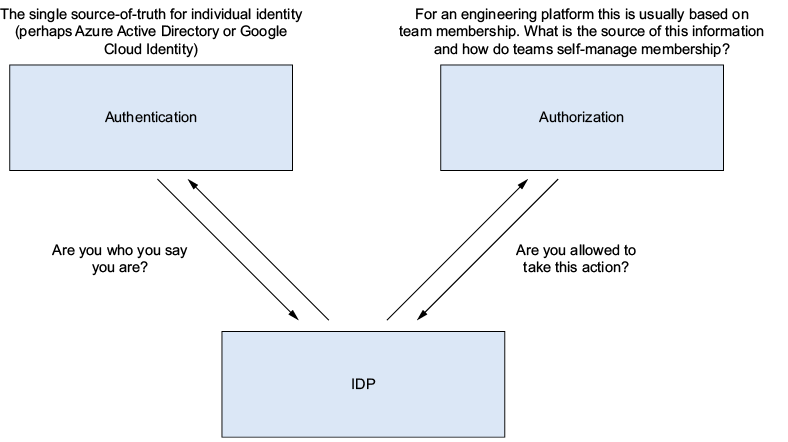
Shows the identity provider acting as a customizable intermediary rather than the sole source of authorization truth. section 4.3.3
