A chief information security officer (CISO) directs cybersecurity strategy while aligning security, governance, compliance, and risk decisions with organizational objectives. The role requires translating complex security issues for technical teams, business stakeholders, financial leaders, and executives. section 5.4
Core responsibilities include:
- Oversee cybersecurity strategy and cybersecurity teams. section 5.6.2
- Ensure compliance with policies and regulations. section 5.6.2
- Communicate cybersecurity risk to the board and executive management. section 5.6.2
- Incorporate business decisions and strategy into cybersecurity planning. section 5.4
Acme Tech governance structure
In a global cloud-based company, the CISO may report to the CEO, CIO, or CTO. That reporting relationship affects how cybersecurity initiatives are prioritized and aligned with strategic goals. The board uses cybersecurity performance metrics to assess resources, protection of critical assets, and ongoing improvement. section 5.6.2
Figure 5.9 The governance structure of our example company, Acme Tech
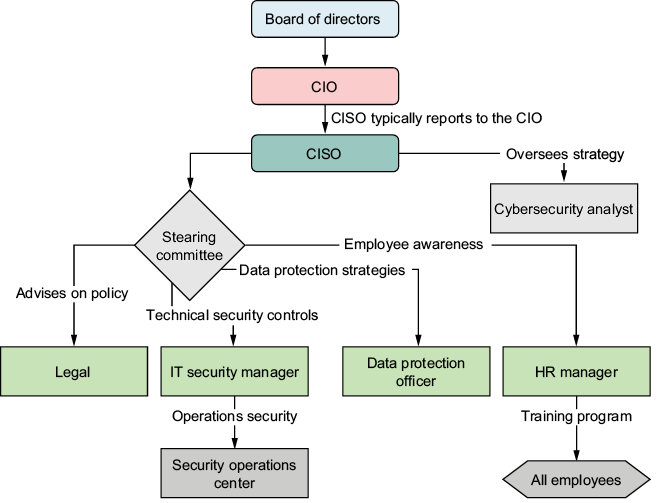
Use the governance structure to trace accountability among the board, executive leadership, the CISO, and cybersecurity operations. section 5.6.2
