The client credentials grant is an OAuth flow for machine-to-machine communication. A nonhuman client directly exchanges its own credentials with an authorization server for an access token, without a browser or repeated user consent. section 7.4.3
Use this flow when the API consumer is a service rather than a person:
- Run automated API calls, such as requests made during continuous integration. section 7.4.3
- Connect services to third-party APIs for email delivery, geolocation, or payment processing. section 7.4.3
- Authenticate internal services communicating across a distributed architecture, such as microservices. section 7.4.3
Scheduled publishing service
A server-side application registered to publish posts on a schedule receives authorization when it is registered. It can then obtain tokens directly whenever it needs to call the API, rather than opening a browser and requesting consent each time. section 7.4.3
Figure 7.8 In the client credentials flow, a server-side application directly exchanges credentials for an access token. If necessary, the resource owner gives consent upon registering the client with the authorization server.
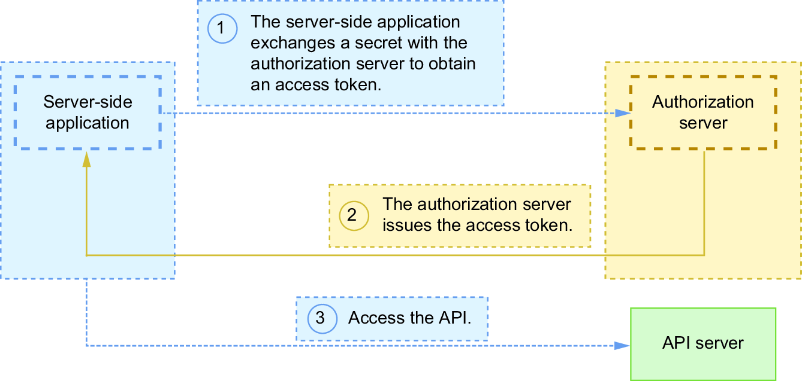
Trace the direct exchange from a server-side application’s credentials to an access token, including registration-time consent when needed. section 7.4.3




