A cloud landing zone is the resource boundary prepared for a service on Anthos. It typically combines one or more Kubernetes namespaces with policies, while non-Anthos resources remain in the service’s own cloud project. section 10.1.1
A landing zone establishes:
- Identity, network configuration, security, and billing controls required before migration or deployment. section 15.3.1
- A tenancy boundary in which each product or tenant deploys only to its assigned namespaces and follows its policies. section 10.3.1
- A network arrangement that can use a shared VPC, separate VPCs, or multiple clusters and regions according to connectivity and resiliency needs. section 10.1.1 section 10.3.1
Migration setup
Before migrating workloads, create the processing environment, define migration sources, and configure the landing zone. Cloud Foundation Toolkit or Terraform can make the foundation repeatable. Discovery tools then identify workloads for migration, after which generated images, Dockerfiles, volumes, and deployment YAML can be tested on GKE or Anthos. section 15.3.1
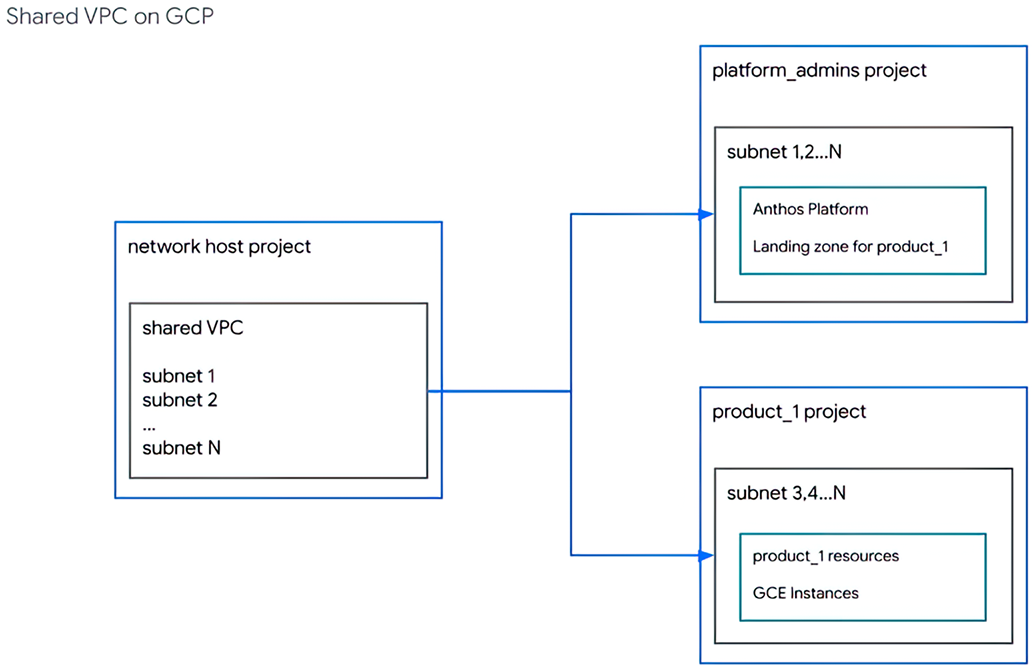
Use the shared VPC architecture to inspect how network resources can remain in a host project while subnets serve multiple service projects. section 10.1.1
