A container breakout escapes container isolation and reaches the host system or resources outside the container. Shared host kernels create an attack path, while a successful breakout may expose the host operating system and other workloads. section 13.2
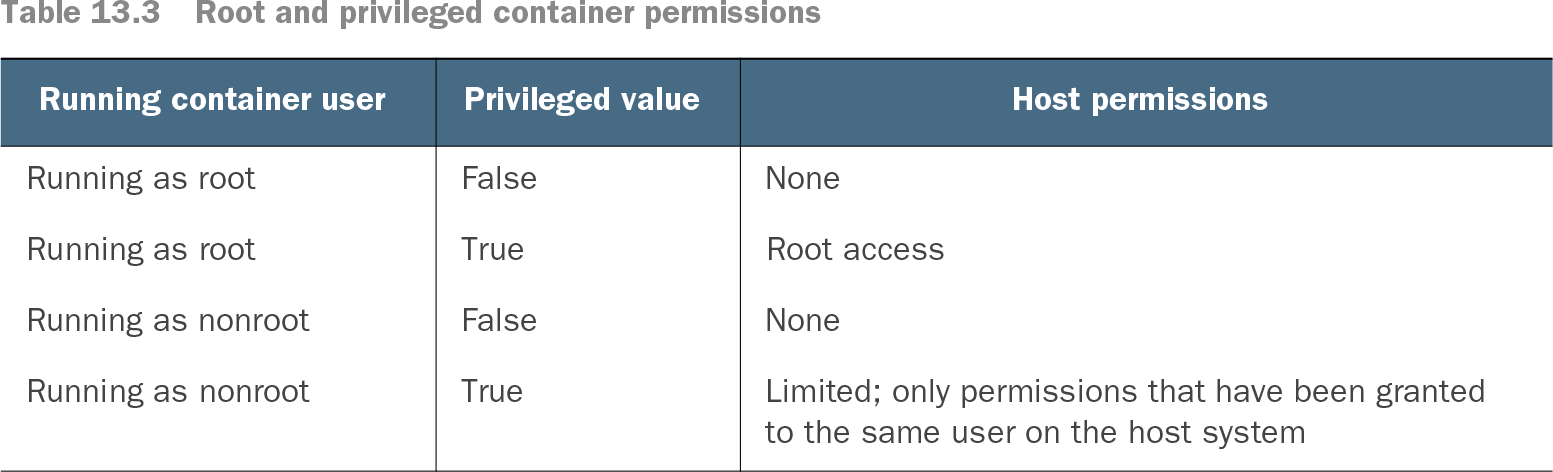
Assess breakout impact through the container's runtime identity and privileges:
- Running as root alone does not grant host-root access; the container runtime and privileged setting determine host permissions. section 13.6
- A root container with privileged mode can receive root access to the host, making host takeover possible after a breakout. section 13.6 section 13.6.1
- Reduce impact by applying least privilege and running applications as nonroot users whenever possible. section 13.6.1
Run a Pod as a nonroot user
A Pod can use securityContext to set runAsUser to 1500, runAsGroup to 1000, and fsGroup to 1200. Commands such as whoami and groups verify the effective identity and group membership. section 13.6.1
Table 13.3 Root and privileged container permissions (view table figure)
| Limited; only permissions that have been granted to the same user on the host system |
Compare running users and privileged settings with their resulting host permissions. section 13.6