Container security protects container images, included packages, runtimes, configurations, and workloads from vulnerabilities and misuse. Container architecture adds convenience but also inherits security risk: even official images may contain serious vulnerabilities that are difficult to see from the image alone. section 3.5
A practical container-security workflow includes:
- Scan images and packages with tools such as Snyk or Docker Scout; review reported vulnerabilities and respond when new problems are discovered. section 3.5
- Inspect exposed ports with docker ps and configure host ports deliberately, including dynamic defaults such as ${API_PORT:-8080}:80. section 3.5
- Reduce runtime exposure with --read-only, resource limits such as --memory and --cpu, and --no-new-privileges. section 3.5
Figure 3.3 Sample results generated by Snyk
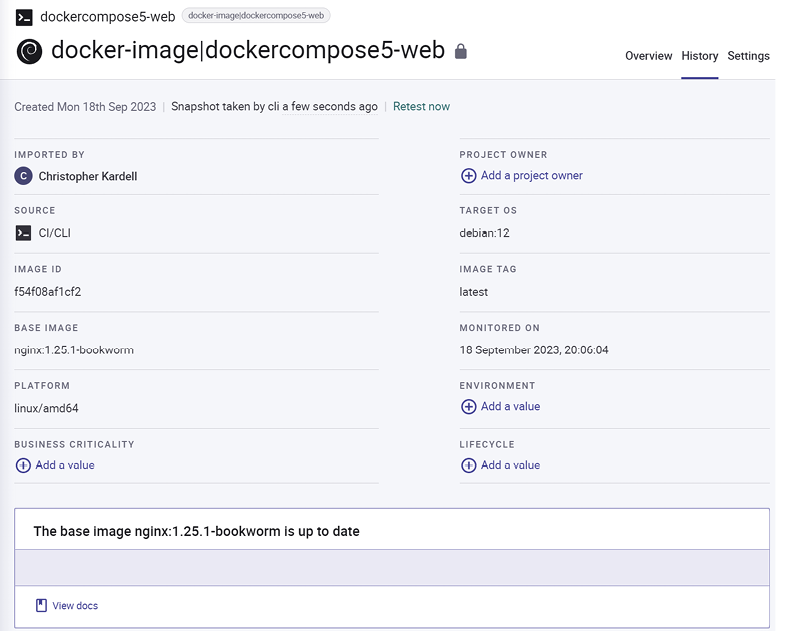
Review a sample Snyk scan to see how image and package vulnerabilities are reported. section 3.5
