Content trust verifies the authenticity and integrity of published software through digital signatures. It connects signed source changes, build artifacts, container images, and software bills of materials to a traceable delivery path. section 4.3.1
A platform can enforce content trust by:
- Requiring developers to use valid personal signing keys and configuring source-control repositories to accept only signed commits. section 4.3.1
- Authenticating CI/CD pipelines, authorizing their access to repositories and registries, and maintaining an auditable log. section 4.3.1
- Requiring signed images and signed software bills of materials that cryptographically verify included packages and image integrity. section 4.3.1
- Providing reusable, versioned pipeline code and self-service configuration so teams satisfy these controls without manual processes. section 4.3.1
Figure 4.7 Steps along the way, from code creation to deployment, can automatically create the necessary provenance.
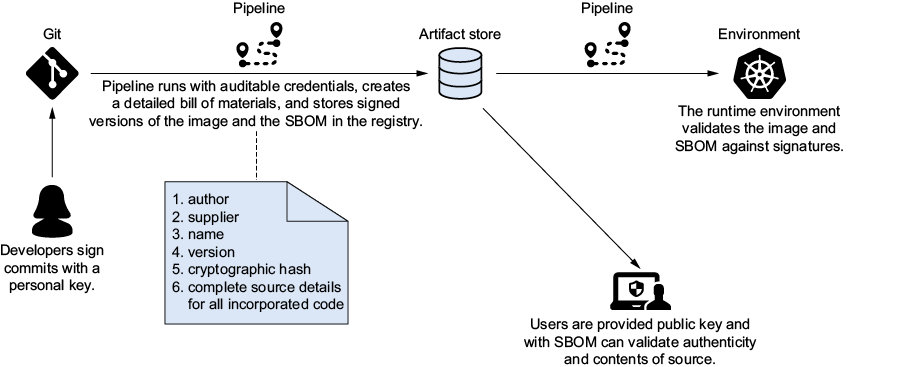
Follow how automated delivery steps create provenance from code creation through deployment. section 4.3.1
