Cosign is an open-source tool for signing and verifying container images and other software artifacts. In a delivery pipeline, signatures provide a verification point before deployment. section 4.3.1
A practical Cosign workflow includes:
- Generate a signing key with Cosign. section 4.3.1
- Sign a Docker image stored in a Docker Trusted Registry-compatible image store. section 4.3.1
- Verify the image signature before deployment, alongside trusted-registry and SBOM checks where required. section 4.3.1
Pipeline verification exercise
Create a Bash script that signs a Docker image with Cosign and validates the resulting signature. Pair that check with an admission policy restricting deployments to images from an approved organization such as ghcr.io/epetech. section 4.3.1
Figure 4.7 Steps along the way, from code creation to deployment, can automatically create the necessary provenance.
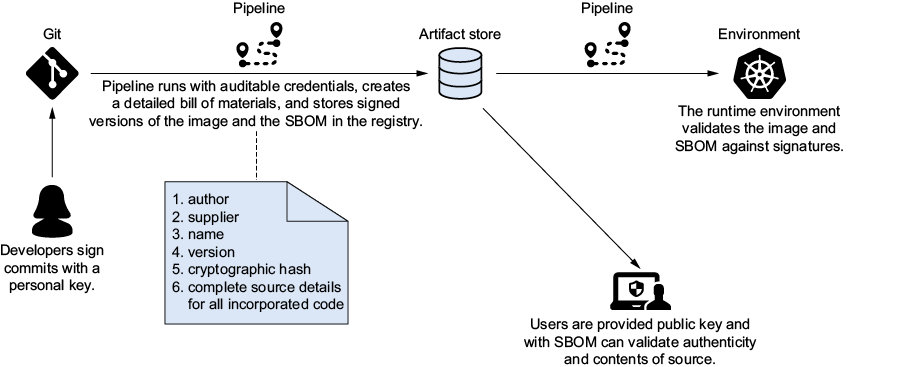
Trace how pipeline steps can automatically create provenance before an executable reaches its target environment. section 4.3.1
