Common Vulnerabilities and Exposures (CVE) is a worldwide catalog and identifier system for publicly reported software and hardware vulnerabilities. CVE entries provide details and recommendations that support vulnerability identification and remediation. section 6.3.1
Use CVEs as a foundation for vulnerability assessment, while recognizing their limits:
- Compare software with known CVEs to identify publicly cataloged vulnerabilities. section 6.3.1
- Combine CVE findings with penetration testing, source code analysis, and configuration reviews to find environment-specific issues. section 6.3.1
- Use CVSS separately to help estimate severity and likelihood; do not treat its score as the complete organizational risk judgment. section 6.3.1
Coverage gap
A custom-built application, internal system, or niche platform may have vulnerabilities without a CVE entry, so CVE results alone can leave important risks unidentified. section 6.3.1
Figure 6.3 Guide for conducting risk assessments
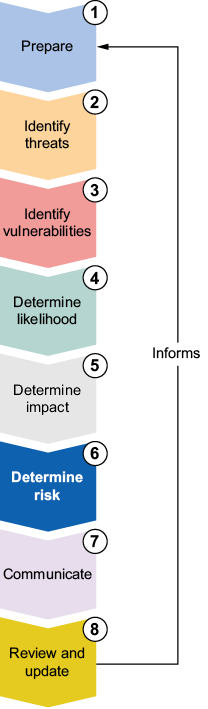
Use the risk-assessment guide to place CVE-based vulnerability identification within the broader sequence of threat, vulnerability, likelihood, and impact analysis. section 6.3.1
