Data access lets a GenAI application retrieve sensitive information at runtime. Common connections include databases, CRMs, document stores, and RAG pipelines. section 4.2
Without runtime data access, manipulated input may produce bad text but has limited impact. With access to live systems, prompt injection can expose sensitive data. A successful leak also requires external communication, such as fetching a URL or rendering an image link. section 4.2 section 4.6
A potential data leak
An application with untrusted input, access to customer records, and a channel for external communication has all three elements of the Lethal Trifecta. Breaking any one element prevents the described attack. section 4.6
Figure 4.2 Security Risk Factors. Each additional factor compounds the risk.
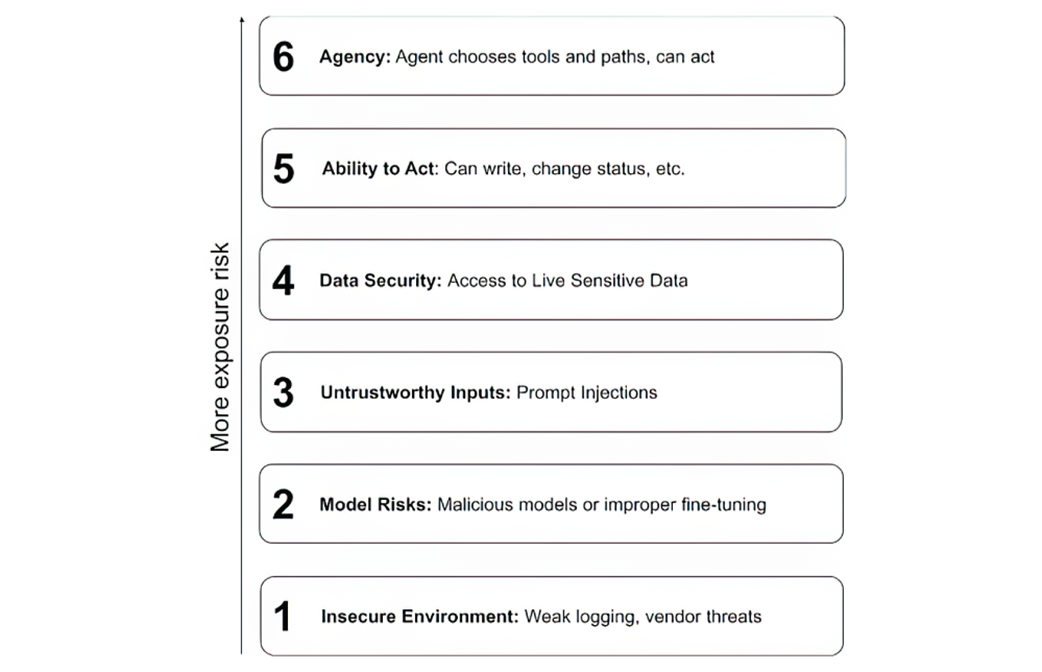
Use the diagram to see data access as one factor in a security risk ladder where additional capabilities compound risk. section 4.2

