Data exfiltration is the unauthorized extraction and transfer of data from an AI system. It compromises confidentiality when sensitive customer information moves to unauthorized parties, including through model training or prompt interactions. section 11.1.1
DataMax recommendation feature
After a data-poisoning incident, an audit finds confidential enterprise-client information in the training process. Prompt logs show that malicious users exfiltrated portions of it, while harmless users may also have encountered leaked data. The exposure followed rushed deployment and weak controls over sensitive inputs. section 11.1.1
A practical response combines governance with technical safeguards:
- Classify data by confidentiality level and trace its movement through training, evaluation, and production use. section 11.1.1
- Restrict access to sensitive inputs, validate training data, encrypt protected information, and monitor for security incidents. section 11.1.1 section 11.6
Figure 11.2 Data classification classifies data into multiple confidentiality levels for a differentiated security strategy.
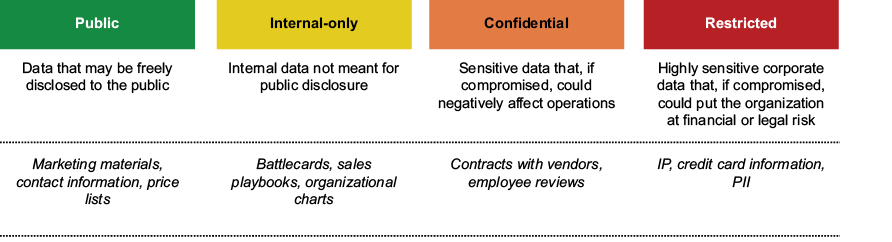
Use the classification diagram to match confidentiality levels with differentiated security controls. section 11.1.1
