Edge gating rejects invalid, abusive, or unauthorized requests before they reach application state-changing logic. Treat it as the first phase of an API request: protect the database from work that should never begin. section 8.4
Apply the gates before touching application state:
- Detect bots with Cloudflare Turnstile or hCaptcha. section 8.4
- Enforce rate limits with fixed-window, token-bucket, or leaky-bucket algorithms keyed by IP or API token. section 8.4
- Validate incoming JSON against a schema using tools such as Zod, Pydantic, or Marshmallow. section 8.4
A booking request
Before a booking request can enter its atomic database transaction, edge gates reject a bot, an over-limit caller, or malformed JSON. Only surviving requests proceed to conflict checks and state changes. section 8.4
Figure 8.6 A typical API request has three phases: synchronous pre-flight checks the user waits for, a core database transaction, and asynchronous follow-up work that runs after the 201 response is sent.
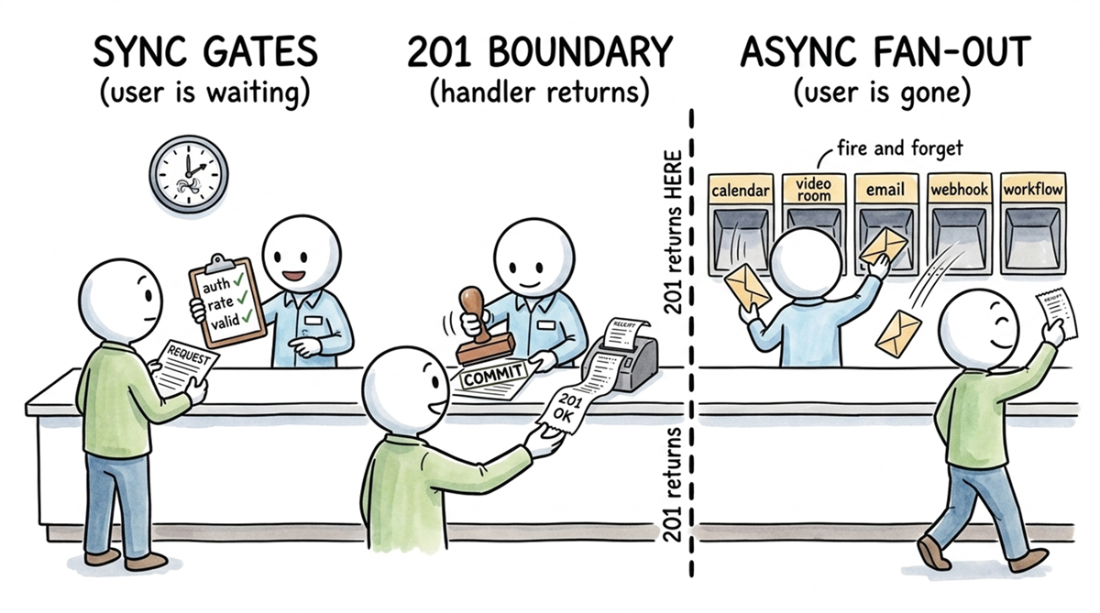
Use the request-phase diagram to distinguish synchronous edge checks from the database transaction and asynchronous follow-up work. section 8.4
