Elliptic Curve Diffie-Hellman (ECDH) lets two parties derive the same shared secret without sending that secret directly. It uses elliptic-curve groups, where recovering a private key from its public key relies on the difficulty of the elliptic-curve discrete logarithm problem. section 5.3 section 5.3.2
A basic ECDH exchange proceeds in named steps:
- Agree on an elliptic curve equation, a finite field, and a generator or base point G. section 5.3.2
- Choose a random private value: Alice chooses a and Bob chooses b. section 5.3.2
- Derive public keys A = [a]G and B = [b]G, then exchange them. section 5.3.2
- Compute the shared secret as [a]B or [b]A; both calculations produce [ab]G. section 5.3.2
- Verify received public keys and add authentication when the exchange must resist an active man-in-the-middle attacker. section 5.5
Alice and Bob derive the same secret
Alice publishes A = [a]G and Bob publishes B = [b]G. Alice computes [a]B, while Bob computes [b]A. Because both equal [ab]G, they obtain the same shared secret even though neither sends a or b. section 5.3.2
ECDH offers much smaller parameters than traditional DH at comparable security levels: 256-bit ECDH parameters provide 128 bits of security, compared with 2,048-bit DH parameters. P-256 and Curve25519 are the most widely used curves described here. section 5.3 section 5.5
Curve selection and validation matter. Standardized choices include P-256 and Curve25519, while invalid received public keys have been a source of many bugs; ECDH is a key exchange, not authentication by itself. section 5.3.3 section 5.5
Figure 5.12 Choosing a private key in ECDH is like choosing an index in a list of numbers produced by a generator (or base point) G. The Elliptic Curve Discrete Logarithm Problem (ECDLP) is to find the index from the number alone.
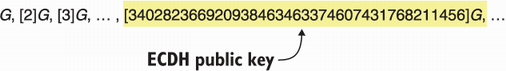
Visualize private-key selection as choosing an index in values generated from the base point G, then compare the public value with the hidden index. section 5.3.2


