An enumeration attack repeatedly calls an API endpoint to discover valid object identifiers or existing records, which can expose further personal data. section 11.6
User-search enumeration
An attacker repeatedly calls GET /api/user/search/{username} to collect existing user IDs, then submits those IDs to POST /stats/workouts/details to retrieve profiles containing age, location, and gender. section 11.6
Figure 11.12 Peloton’s user search endpoint could be exploited to enumerate existing users and pull their details. The signature of this type of abuse is the repeated number of calls against the same endpoint to scrape the data.
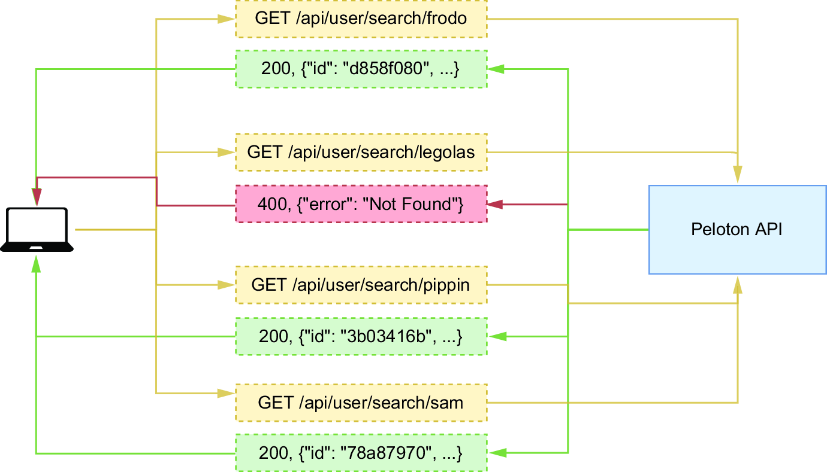
The figure shows the endpoint sequence and the repeated-call signature used to scrape existing users. section 11.6
Detect the pattern through endpoint-level observability:
- Track request counts for individual endpoints, because a single log event may not reveal enumeration. section 11.6
- Use OpenTelemetry counters to record endpoint activity and make repeated calls measurable. section 11.6
