Execute permission grants the ability to invoke a specified SQL Server routine or procedure. For xp_cmdshell, it is one possible route to execution, alongside sysadmin membership and CONTROL SERVER. section 14.4 section 14.4
Treat direct execute grants as security-sensitive because they can be less visible than role membership.
- Check beyond sysadmin membership: direct CONTROL SERVER, EXECUTE, or IMPERSONATE permissions may create opaque access paths. section 14.4
- Do not assume disabling xp_cmdshell removes the risk; an account with sufficient authority can enable it again. section 14.4
The restricted-OS DBA
A DBA barred by company policy from operating-system access may use xp_cmdshell as a back door to the operating system, turning an execute grant into a policy and lateral-movement concern. section 14.4
Lateral movement
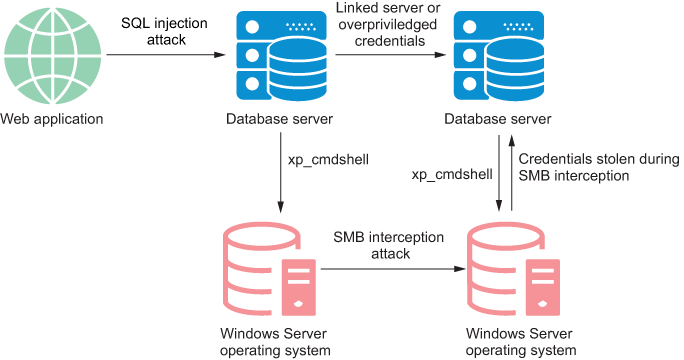
Use the lateral-movement figure to connect routine execution permissions with broader operating-system security exposure. section 14.4
