A grant type is an OAuth 2.0 authorization flow for obtaining an access token in a particular scenario. Choosing the right flow helps an application delegate API access without sharing a user's credentials. section 25.1.3
Common OAuth 2.0 grant types include:
- Authorization code: lets an application exchange an authorization code and secret for a token after a user interaction. section 25.1.3
- Authorization code with PKCE: adds protections against certain attacks and should be preferred when possible. section 25.1.3
- Client credentials: supports machine-to-machine access when no user is involved, such as one API calling another. section 25.1.3 section 25.7
Delegating access to photos
When dogphotos.com needs access to a user's Facebook photos, the user signs in to Facebook rather than giving dogphotos.com their Facebook credentials. OAuth 2.0 grants dogphotos.com permission to call the photos API on the user's behalf. This is authorization, not authentication: the application receives delegated access, not necessarily the user's identity. section 25.1.3
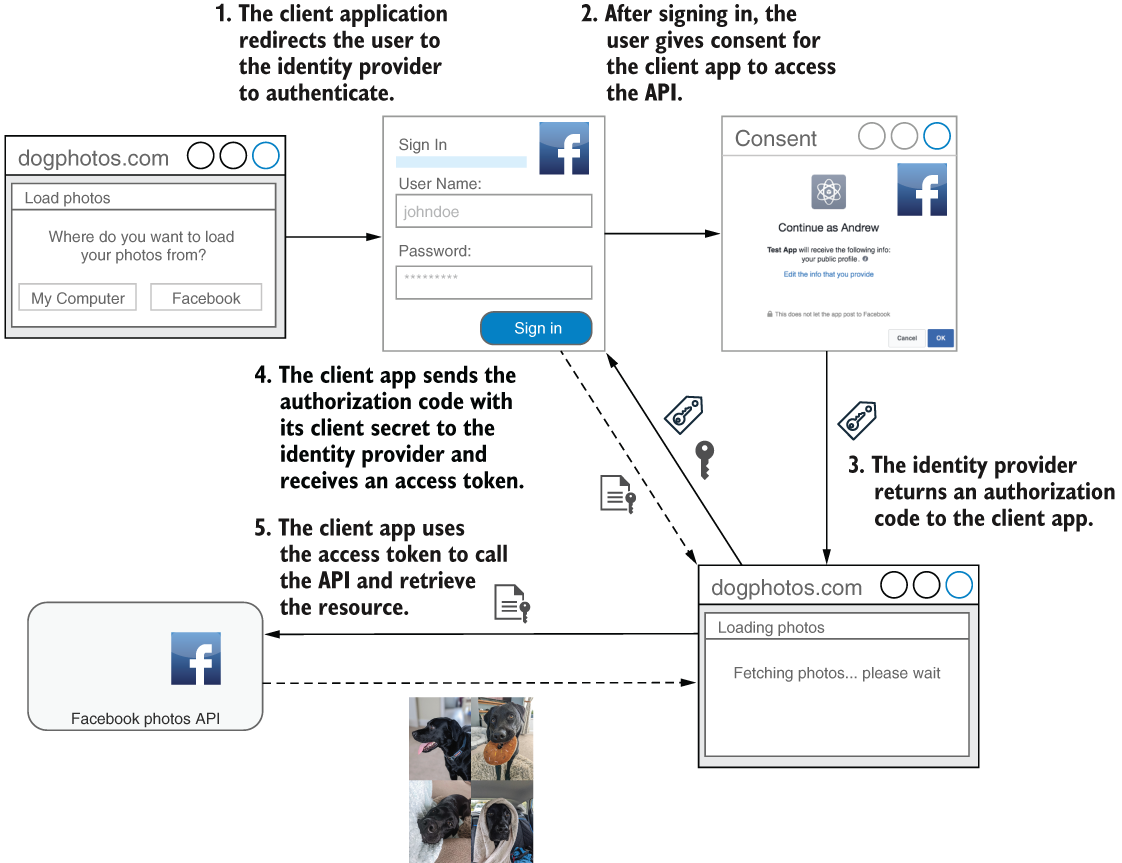
Follow the authorization-code flow from the user's interaction through delegated access to the photos API. section 25.1.3

