HOTP is a one-time-password algorithm that uses a shared symmetric key and a counter to produce authentication codes. Unlike a reusable password, each generated code is intended for one use. HOTP is standardized in RFC 4226. section 11.2.3
Its authentication arrangement has three important parts:
- The client and server share a usually 16- to 32-byte uniformly random symmetric key. section 11.2.3
- A counter supplies HOTP’s additional data when generating each code. section 11.2.3
- Both sides must retain compatible counter state; falling out of synchronization can prevent legitimate codes from being generated or validated. section 11.2.3
Figure 11.7 A one-time password (OTP) algorithm allows you to create as many one-time passwords as you want from a symmetric key and some additional data. The additional data is different, depending on the OTP algorithm.
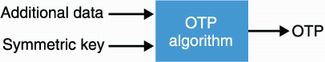
Visualizes how a symmetric key and additional data become successive one-time passwords, with the additional data distinguishing HOTP from time-based OTP. section 11.2.3
