A hypertree is a tree of Merkle trees: its upper-level leaves authenticate the root hashes of lower-level trees, each containing one-time-signature keys. section 14.2.3
In XMSSMT, the structure helps balance signature capacity against signing and key-generation work:
- Use smaller trees whose leaves authenticate the roots of other Merkle trees. section 14.2.3
- Regenerate only the trees along the path to the one-time-signature leaf used for a message. section 14.2.3
- Track state carefully in XMSSMT: reusing a path can reuse a one-time-signature key and enable forgery. section 14.2.3
Figure 14.6 The XMSSMT stateful hash-based signature scheme uses multiple trees to increase the amount of signatures supported by the scheme while reducing the work at key generation and signing time. Each tree is deterministically generated only when they are used in the path to the final leaf that contains the OTS used to sign a message.
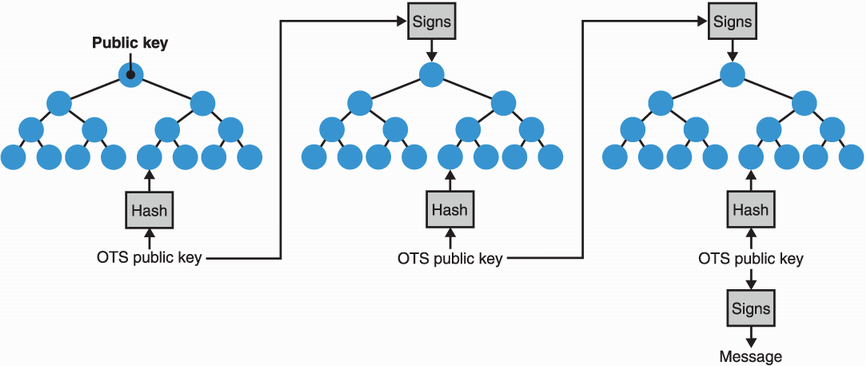
A layered diagram shows how XMSSMT increases supported signatures while generating only the trees needed along the selected path. section 14.2.3
