A reasonable likelihood of a link between an AI system and an incident starts the reporting clock; confirmed root cause is not required. Deployer and provider duties are distinct, and corrective action runs alongside reporting. section 7.5.2
Apply the reporting path:
- When a deployer spots a qualifying pattern, it must immediately notify the provider, importer or distributor, and relevant market surveillance authority. Draft guidance interprets “immediately” as within 24 hours. section 7.5.2
- The provider carries the formal reporting obligation and corrective action duty. A GPAI model with systemic risk reports to the AI Office instead of the national market surveillance authority. section 7.5.2
Triage a recurring failure
ClaimAssist wrongfully denied favorable payment-plan terms to dozens of applicants with a chronic condition. The pattern persisted for months, affecting people who did not challenge the terms; it likely crosses the serious-incident threshold on grounds including indirect health harm. section 7.5.2
Figure 7.14 EU AI Act incident reporting tiers. Clock starts at reasonable likelihood of a causal link, not confirmed root cause.
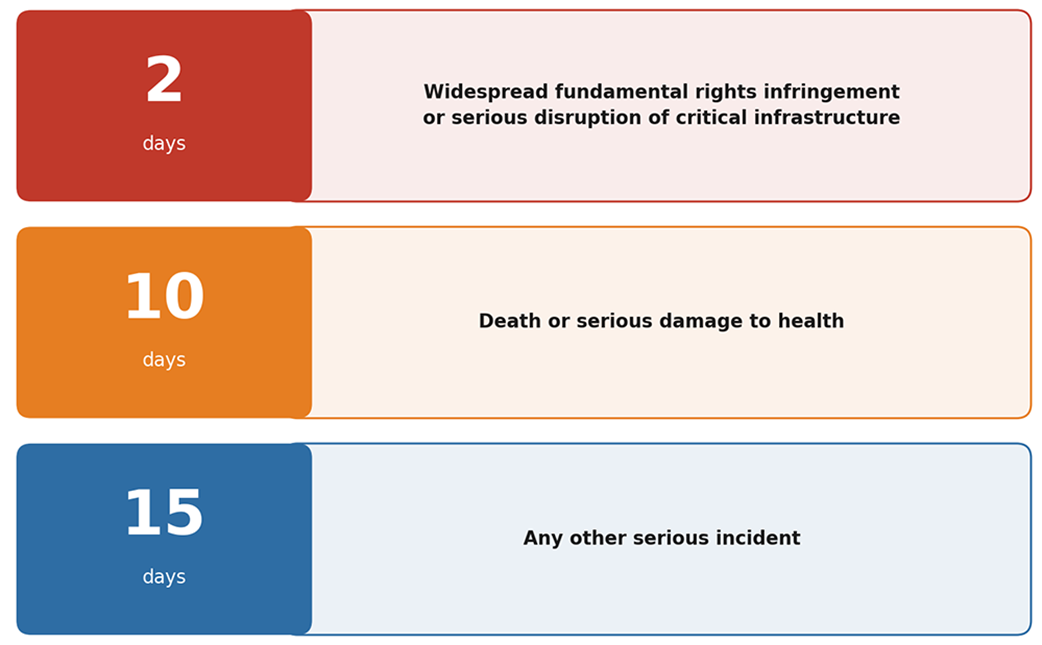
Use the reporting-tier figure to review when the clock starts and how incident reports are routed. section 7.5.2
