Intel Software Guard Extensions (SGX) is a trusted execution environment (TEE): CPU-enforced isolation keeps enclave data and execution separate from the normal operating system. Its practical target is confidential computing, especially running client code on cloud servers that should not see or tamper with it. section 13.2.5
Trust in an SGX deployment depends on several pieces:
- Local attestation lets enclaves on one platform prove to each other that they are secure enclaves. section 13.2.5
- Remote attestation lets a client verify that a legitimate remote enclave produced a response rather than an impersonator. section 13.2.5
- Each SGX chip receives unique root sealing key pairs during manufacturing, with the public key signed by an Intel certificate authority. section 13.2.5
Cloud privacy
A client can send sensitive computation to a cloud server while using an SGX enclave to keep the code and its data hidden from the server. section 13.2.5
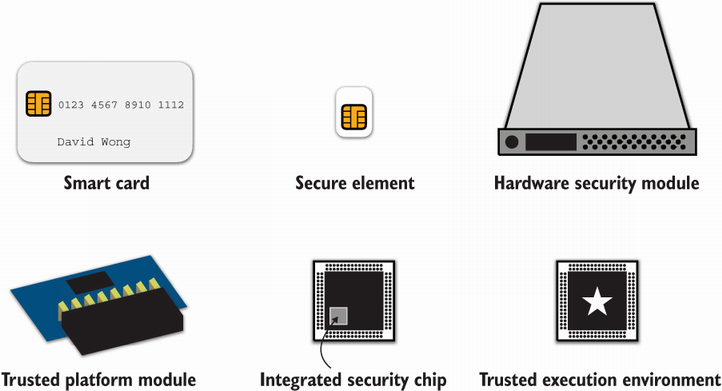
Figure 13.4 The different hardware solutions you learned in this chapter and an idea of what they look like.
Compare SGX with TEEs, TPMs, secure elements, HSMs, and other hardware security solutions by form factor, speed, and security level. section 13.3
