An aspect is a modular unit that intercepts selected method calls and adds behavior around them. In method security, it evaluates authorization rules before or after delegation and prevents unauthorized calls or results from reaching the caller. section 11.1.1
Spring Security uses aspects to separate authorization responsibilities from business logic:
- Preauthorization checks rules before the protected method executes and refuses delegation when they fail. section 11.1.1
- Postauthorization delegates the call, checks the result afterward, and prevents unauthorized values from returning. section 11.1.1
- Prefiltering intercepts a collection argument and removes values that fail an authorization expression before business processing. section 12.1
Filtering products before selling
A service method annotated with @PreFilter("filterObject.owner == authentication.name") receives only products owned by the authenticated user. The aspect changes the supplied mutable collection, leaving the service method focused on selling products. Immutable collections cause an UnsupportedOperationException. section 12.1
Figure 11.2 When we enable global method security, an aspect intercepts the call to the protected method. If the given authorization rules aren’t respected, the aspect doesn’t delegate the call to the protected method.
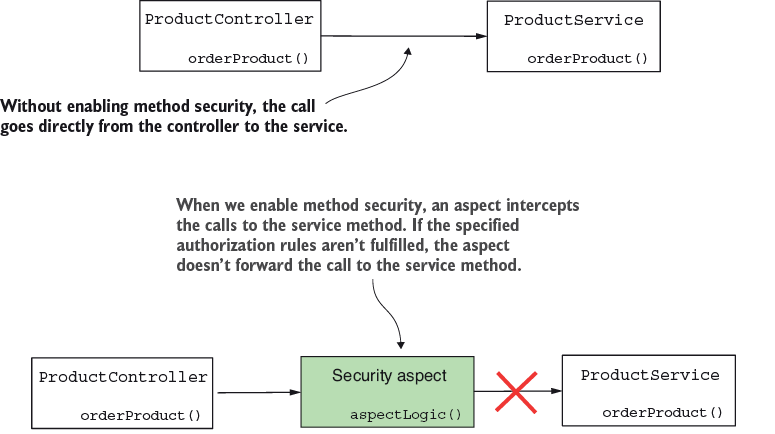
The interception flow shows how an aspect blocks an unauthorized method call instead of delegating to the protected method. section 11.1.1

