liveBook · Manning

Internal fraud

As explained in Financial AI in Practice

Internal fraud is fraud committed by people within an organization, such as employees misappropriating funds or stealing customer data.

Internal fraud is illicit activity by people inside an institution. Examples include employees misappropriating company funds through embezzlement or stealing customer data for personal gain. It targets the institution itself, unlike market manipulation, which aims to deceive the broader financial market. section 7.2

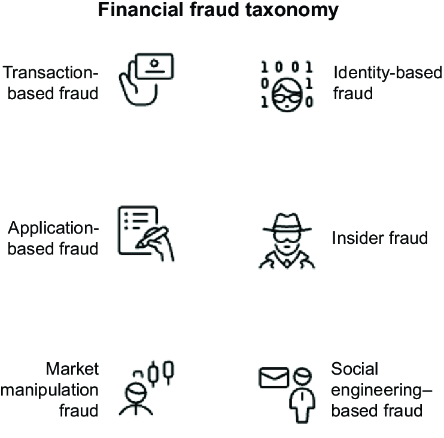
Figure 7.2 A structured typology of financial fraud. This framework organizes fraud into six primary categories based on the core attack vector, such as exploiting a transaction, compromising an identity, or deceiving a person. This structured view is crucial for developing specific and effective AI-driven countermeasures for each type of threat.
figure

The financial-fraud typology places internal fraud among six categories organized by core attack vector. section 7.2

How Financial AI in Practice covers it

How deep it goes
Defines internal fraud and gives two examples, but does not detail detection methods or implementation.
Examples
Uses employee embezzlement and theft of customer data for personal gain as examples.
What you can do after
Design targeted detection strategies by organizing financial fraud categories around their core attack vectors.
How it connects
Connects internal fraud to embezzlement, employee fraud, and market manipulation as a contrasting fraud category.

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Financial AI in Practice. The section links point to the parts of the book it draws on.