In a Cisco IOS extended ACL, the ip keyword matches every IPv4 packet, regardless of its encapsulated protocol. Use it when filtering should depend only on source and destination IP addresses. section 24.1.1
Apply the keyword within an extended ACL entry:
- permit ip any any allows all IPv4 packets from every source to every destination. section 24.1.1
- permit ip host 172.16.1.1 any allows all IPv4 traffic from one host to any destination. section 24.1.1
- Remember that an ACE must match its protocol, source, and destination values; ip does not bypass the address conditions. section 24.1.1
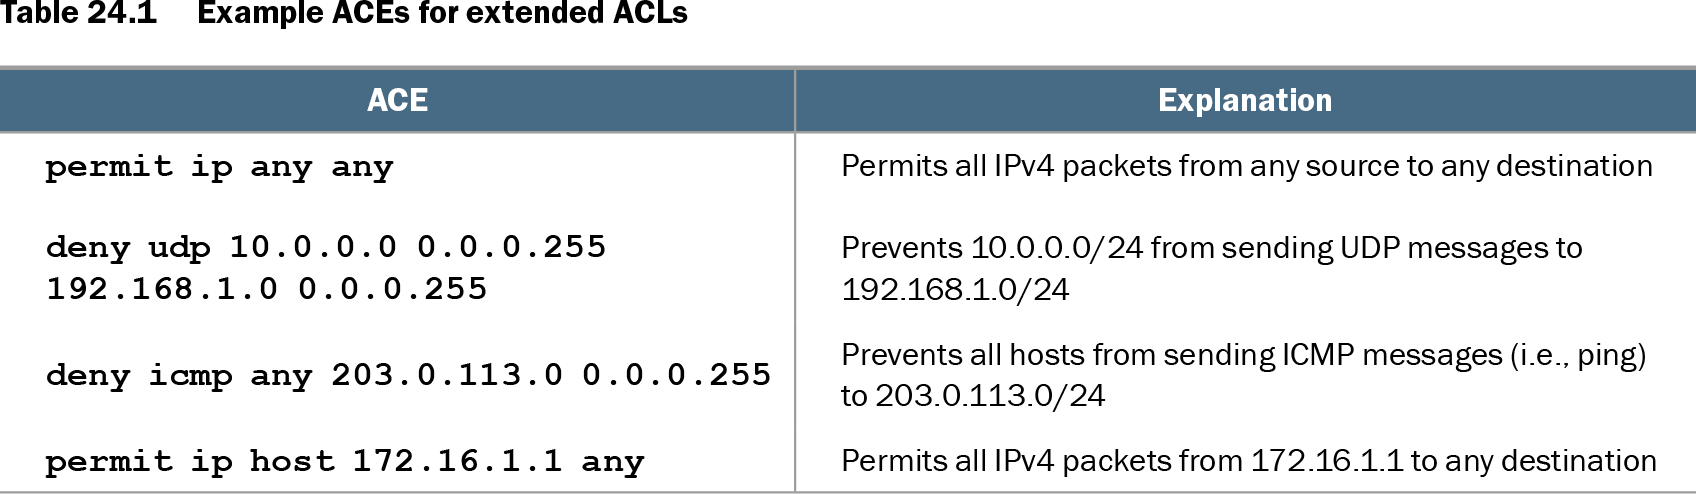
Table 24.1 Example ACEs for extended ACLs (view table figure)
| ACE |
Explanation |
|---|---|
| permit ip any any |
Permits all IPv4 packets from any source to any destination |
| deny udp 10.0.0.0 0.0.0.255 192.168.1.0 0.0.0.255 |
Prevents 10.0.0.0/24 from sending UDP messages to 192.168.1.0/24 |
| deny icmp any 203.0.113.0 0.0.0.255 |
Prevents all hosts from sending ICMP messages (i.e., ping) to 203.0.113.0/24 |
| permit ip host 172.16.1.1 any |
Permits all IPv4 packets from 172.16.1.1 to any destination |
Compare ip with protocol-specific ACEs such as udp and icmp. section 24.1.1