IP masking hides an origin server’s public network address behind an intermediary. With a CDN, users connect to the edge, which serves cached content or forwards requests to the origin. section 12.1.3
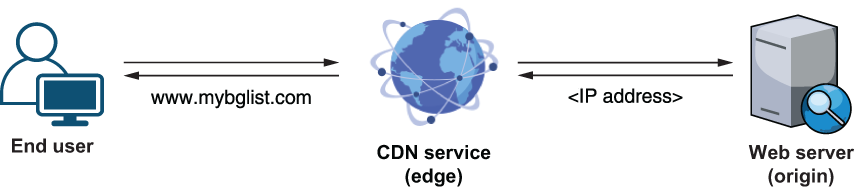
The edge-origin pattern shows how a public CDN endpoint can serve an API without directly exposing its origin server. section 12.1.3
A practical Cloudflare configuration uses these steps:
- Create an A record for a deployment subdomain, such as win-01, pointing to the Azure VM public IP. section 12.2.3
- Set Proxy status to Proxied and TTL to Auto, so the subdomain resolves to Cloudflare rather than directly to the VM. section 12.2.3
- Use only the proxied custom subdomain publicly; keep the Azure-managed DNS name hidden because it resolves directly to the VM. section 12.2.3
Checking the masked endpoint
Open the proxied HTTP or HTTPS subdomain after saving the record. A 522 Connection timed out response from Cloudflare indicates that Cloudflare is handling the request but cannot reach the origin, such as when no web server listens on ports 80 or 443. section 12.2.3

