A kernel filesystem is a kernel-provided interface, commonly mounted under /proc or /sys, that exposes information or controls for kernel-managed resources. Containers generally need to read these filesystems, but unrestricted writes could compromise the host. Podman therefore limits, masks, or mounts selected kernel filesystems read-only. section 10.1 section 1.2
Podman applies several boundaries to kernel filesystem access:
- Mounts /sys, /sys/fs/cgroup, and /sys/fs/selinux read-only while providing a namespaced /proc inside the container. section 10.1
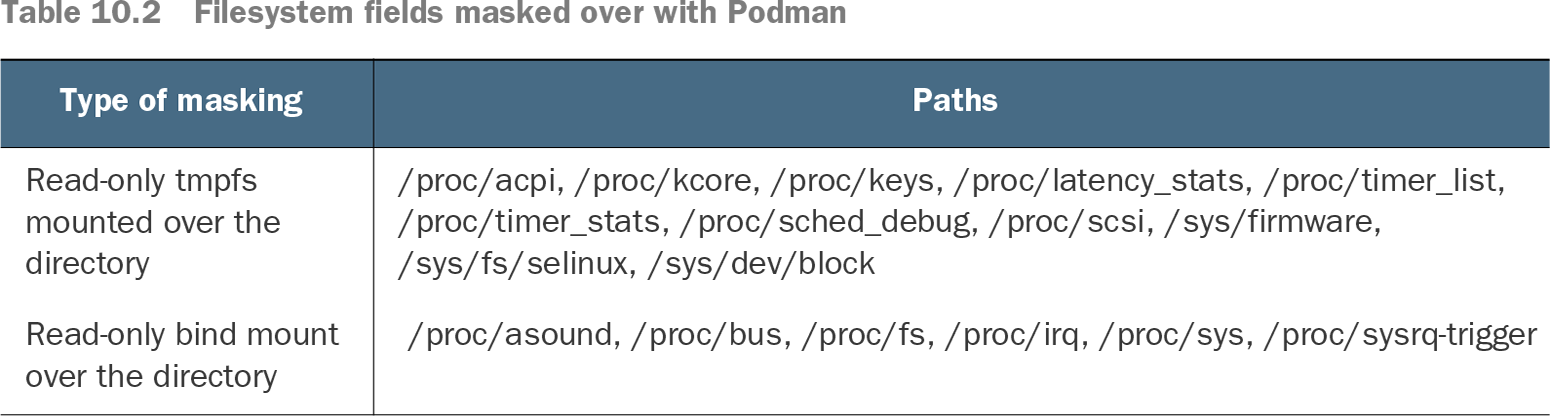
- Masks sensitive paths such as /proc/kcore, /proc/keys, /proc/sys, and /sys/firmware with read-only temporary or bind mounts. section 10.1
- Combines filesystem restrictions with mount namespaces, SELinux, capabilities, seccomp, and user namespaces rather than defaulting to --privileged. section 10.0 section 1.2
Container access boundary
A process inside a PID namespace sees the container’s /proc rather than the host’s /proc and can affect only processes within that namespace. An application needing a masked directory may require carefully scoped additional access. section 10.1
Table 10.2 Filesystem fields masked over with Podman (view table figure)
Browse the complete list of filesystem paths Podman masks and the mount treatment applied to each. section 10.1