Layered security control protects important assets with multiple defenses placed one after another. Rather than trusting a single switch, service, or guard, it creates backup and redundancy across the environment. section 6.1.1
A castle with very good security instincts
Imagine a castle protected by a gatehouse, moat, drawbridge, outer wall, inner wall, keep, and guards. If one defense fails, others still stand between an attacker and the treasure. Azure applies the same defense-in-depth idea to protect data, beginning with physical facilities and identity controls. section 6.1.1
Figure 6.2 The seven layers of castle defense
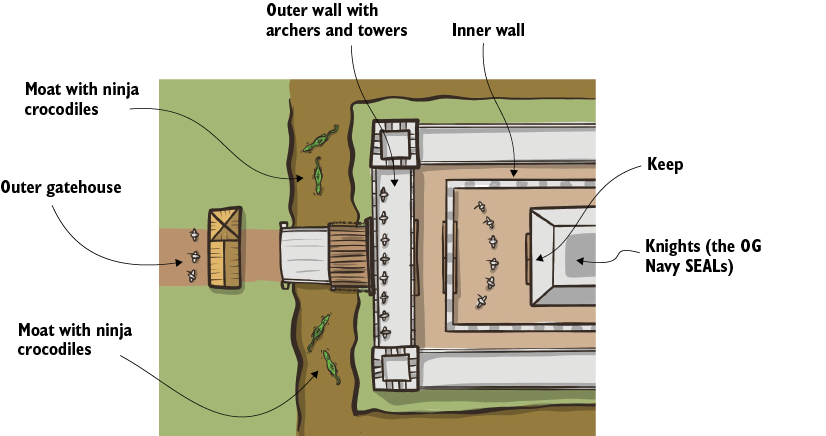
Use the castle diagram to see how successive controls combine into defense in depth. section 6.1.1
Figure 6.3 Azure layers of defense in depth
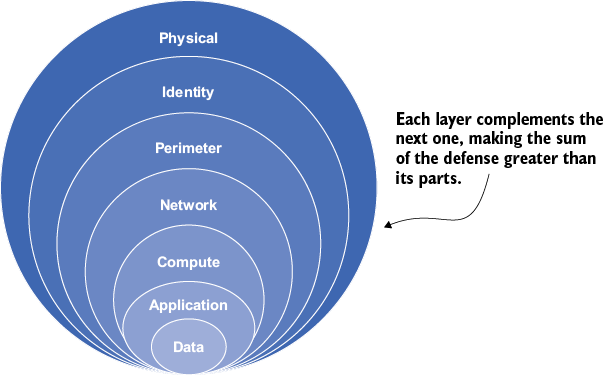
Use the Azure diagram to connect the castle analogy with layered protection for cloud data. section 6.1.1
