Manually Authenticated Diffie-Hellman (MA-DH) strengthens a Diffie-Hellman key exchange against an active man-in-the-middle attacker. Devices compare a short authenticated string (SAS), but first commit to public keys so neither side can choose a key after seeing the other’s. section 11.3.3
A secure SAS-based exchange works in three steps:
- Alice sends a commitment to her public key. section 11.3.3
- Alice receives Bob’s public key, then reveals her committed public key. section 11.3.3
- Both devices derive an SAS and the user compares the displayed values; matching values indicate that the exchange was not MITM’d. section 11.3.3
Pairing a phone with a car
Bluetooth Numeric Comparison can display an SAS during pairing. The short value is convenient for real-time comparison, unlike a long fingerprint, though Bluetooth security was noted as broken by the KNOB attack as of 2021. section 11.3.3 section 11.3.3
Figure 11.17 The diagram on the left pictures a secure SAS-based protocol in which Alice first sends a commitment of her public key. She then only reveals her public key after receiving Bob’s public key. As she committed to it, she cannot freely choose her key pair based on Bob’s key. If the exchange is actively MITM’d (diagram on the right), the attacker cannot choose either key pairs to force Alice’s and Bob’s SAS to match.
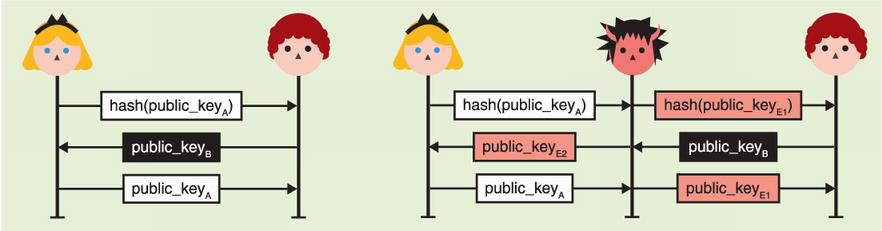
Shows how committing before revelation prevents an attacker from selecting public keys that force both devices to display the same SAS. section 11.3.3
