The METRICS methodology is a structured process for designing, implementing, and maintaining a cybersecurity metrics program aligned with business goals. Its seven stages are Measure, Evaluate, Threshold, Report, Improve, Communicate, and Sustain. section 3.2 section 3.7
Figure 3.2 The METRICS methodology for designing, implementing, and sustaining a security metrics program
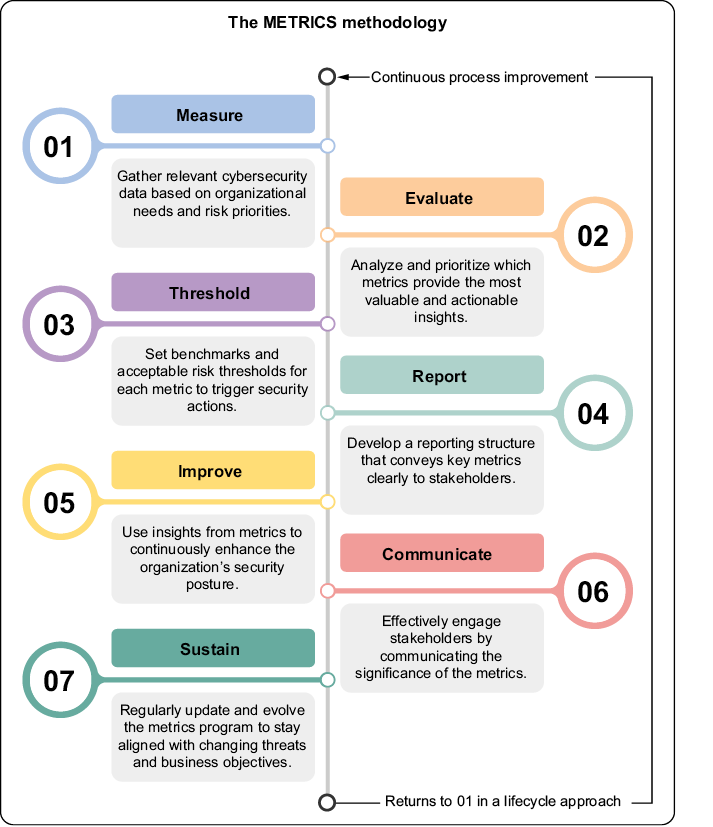
A process diagram clarifies how the seven stages form a repeatable cycle for designing, implementing, and sustaining a security metrics program. section 3.2
Use the methodology to turn security data into decisions:
- Measure relevant security performance data rather than collecting raw counts without purpose. section 3.0
- Evaluate the value of the metrics, set thresholds, and report results in forms suited to different stakeholders. section 3.7
- Improve the security posture and communicate risk through dashboards and actionable analysis. section 3.0 section 3.7
- Sustain the program by revisiting measurements, adjusting thresholds, and evolving reports as risks, regulations, technologies, and business goals change. section 3.2.7
PharmaSecure
A life sciences company subject to SOC2 and HIPAA uses METRICS to measure critical security data, evaluate its value, set thresholds, build risk reporting, improve its posture, and sustain compliance through ongoing updates. section 3.3 section 3.3.8
