A potential breach assessment evaluates security gaps or misconfigurations that could enable unauthorized access or data compromise without an incident having occurred. It differs from a breach, which confirms unauthorized access or compromise and requires immediate response and mitigation. section 9.1
Use potential breach assessment to expose weaknesses before they become incidents:
- Review changes that may expose sensitive data without authentication or authorization, especially when required stakeholders or security threat and risk assessment are omitted. section 9.1
- Apply regular security assessments, security audits, and penetration tests to identify exploitable gaps early and prevent escalation. section 9.1
A risky production change
An engineering team changes a live system without approval, documentation, or a security assessment. The change exposes sensitive data without proper authorization. No compromise is confirmed, so the issue requires potential breach assessment rather than breach response. section 9.1
Figure 9.1 Steps to develop a comprehensive incident response plan
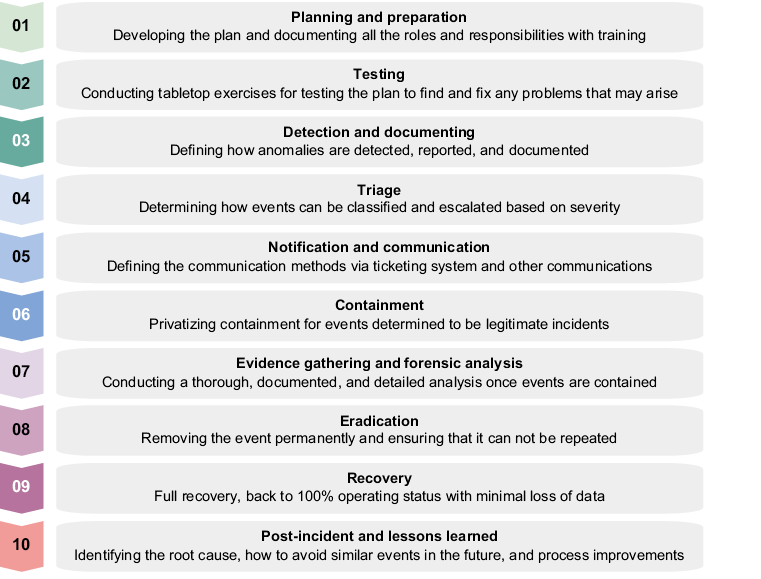
Place potential breach assessment within incident management alongside planning, testing, detection, triage, containment, recovery, and lessons learned. section 9.1
