liveBook · Manning

Namespace exemption

As explained in Google Anthos in Action

A namespace exemption is a configuration that excludes resources in a Kubernetes namespace from specified policy processing.

A namespace exemption keeps selected Kubernetes resources out of Gatekeeper policy processing. It is useful when a cluster-wide constraint would block legitimate system Pods: a privileged-container policy, for example, could prevent kube-proxy or a networking agent from starting. section 13.4.1

Choose the narrowest exemption that permits the workload:

  • For Gatekeeper-wide processing, use a Config object to name excluded namespaces. Set processes to * to exclude them from all processing, or select audit, webhook, or sync individually. section 13.4.1
  • To exclude namespaces from a particular constraint, place excludedNamespaces in that constraint’s match configuration. section 13.4.1
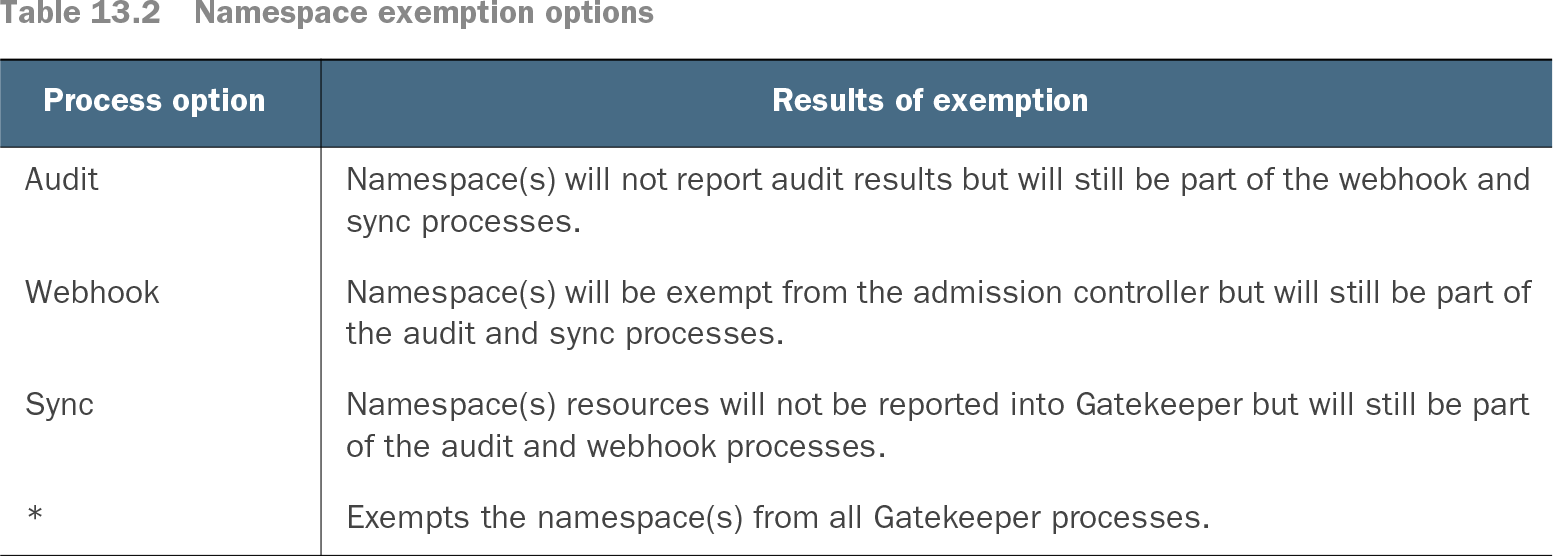
Table 13.2 Namespace exemption options (view table figure)

Process option

Results of exemption

Audit

Namespace(s) will not report audit results but will still be part of the webhook and sync processes.

Webhook

Namespace(s) will be exempt from the admission controller but will still be part of the audit and sync processes.

Sync

Namespace(s) resources will not be reported into Gatekeeper but will still be part of the audit and webhook processes.

*

Exempts the namespace(s) from all Gatekeeper processes.

Compare the process options before configuring an exemption: excluding audit results does not also exclude admission-webhook or sync processing. section 13.4.1

apiVersion: config.gatekeeper.sh/v1alpha1
kind: Config
metadata:
  name: config
  namespace: "gatekeeper-system"
spec:
  match:
    - excludedNamespaces: ["kube-system", "gatekeeper-system"]
      processes: ["*"]

This Config exempts kube-system and gatekeeper-system from every Gatekeeper process with processes: ["*"]. section 13.4.1

How Google Anthos in Action covers it

How deep it goes
Shows Config-based and constraint-level exclusions, with distinct audit, webhook, sync, and all-process scopes.
Examples
Uses kube-proxy and a networking agent as affected Pods, plus a Config manifest exempting two system namespaces.
What it assumes
Assumes familiarity with Kubernetes namespaces and policy constraints rather than teaching those concepts from zero.
What you can do after
Operate/configure Gatekeeper exemptions for selected namespaces, constraints, or processing stages.
How it connects
Connects namespace exemptions to Gatekeeper constraints, admission controllers, auditing, and privileged-container policies.

This explainer was generated by Manning's knowledge graph from the text of Google Anthos in Action. The section links point to the parts of the book it draws on.