Network isolation restricts communication paths so protected systems remain reachable only through permitted network boundaries. In MongoDB Atlas, it forms part of the continuously enforced security controls and depends on deliberate connectivity configuration. section 20.1 section 20.7
Configure Atlas network isolation with layered boundaries:
- Place the Atlas cluster in a virtual private cloud and control permitted traffic with IP access lists. section 20.7
- Use private endpoints for additional isolation, keeping application-to-Atlas traffic within the cloud provider’s private network rather than traversing the public internet. section 20.7
- Treat isolation as one layer alongside firewalls, authentication, authorization, encryption, intrusion detection, and auditing. section 20.7
Figure 20.1 The shared responsibility model in Atlas divides security and operational tasks among customers, MongoDB, and the underlying cloud providers (AWS, GCP, and Azure). (Image © MongoDB 2024 CC BY-NC-SA 3.0)
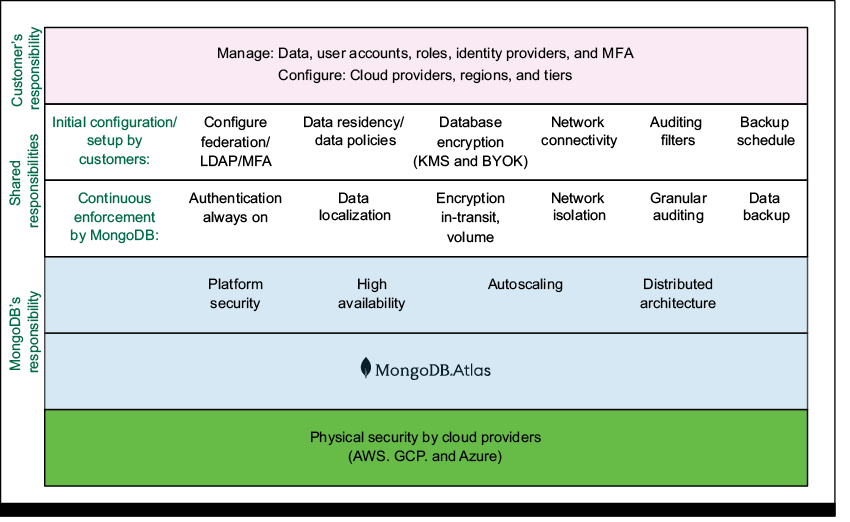
Use the shared-responsibility diagram to distinguish customer-configured network connectivity from MongoDB’s ongoing enforcement and cloud-provider infrastructure responsibilities. section 20.1

