NIST SP 800-30 provides a consistent, repeatable framework for identifying, analyzing, and evaluating organizational risks. It connects threats, vulnerabilities, likelihood, exploitability, and effects to control selection, prioritization, and residual-risk decisions. section 6.3
A practical assessment follows these concerns:
- Set the scope and define its assets, boundaries, systems, and data to prevent scope creep. section 6.3.1
- Identify realistic, current, and potential threats rather than exaggerated scenarios. section 6.3.1
- Determine vulnerabilities using software analysis and known CVEs, while recognizing that proprietary systems may lack entries. section 6.3.1
- Assess likelihood, exploitability, and effects; then prioritize controls and identify residual risks. section 6.3
Figure 6.3 Guide for conducting risk assessments
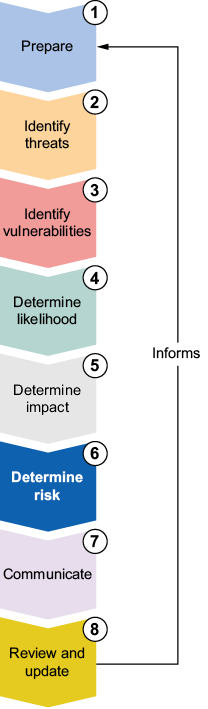
Use the assessment guide to follow the framework’s sequence and connect preparation, threat and vulnerability analysis, and risk decisions. section 6.3.1
